|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Ubuntu Local Security Checks >> USN222-2 : perl vulnerability Vulnerability Assessment Details
|
USN222-2 : perl vulnerability |
||
|
perl vulnerability Detailed Explanation for this Vulnerability Assessment Summary : These remote packages are missing security patches : - libcgi-fast-perl - libperl-dev - libperl5.8 - perl - perl-base - perl-debug - perl-doc - perl-modules - perl-suid Description : USN-222-1 fixed a vulnerability in the Perl interpreter. It was discovered that the version of USN-222-1 was not sufficient to handle all possible cases of malformed input that could lead to arbitrary code execution, so another update is necessary. Original advisory: Jack Louis of Dyad Security discovered that Perl did not sufficiently check the explicit length argument in format strings. Specially crafted format strings with overly large length arguments led to a crash of the Perl interpreter or even to execution of arbitrary attacker-defined code with the rights of the user running the Perl program. However, this attack was only possible in insecure Perl programs which use variables with user-defined values in string interpolations without checking their validity. Solution : Upgrade to : - libcgi-fast-perl-5.8.7-5ubuntu1.2 (Ubuntu 5.10) - libperl-dev-5.8.7-5ubuntu1.2 (Ubuntu 5.10) - libperl5.8-5.8.7-5ubuntu1.2 (Ubuntu 5.10) - perl-5.8.7-5ubuntu1.2 (Ubuntu 5.10) - perl-base-5.8.7-5ubuntu1.2 (Ubuntu 5.10) - perl-debug-5.8.7-5ubuntu1.2 (Ubuntu 5.10) - perl-doc-5.8.7-5ubuntu1.2 (Ubuntu 5.10) - perl-modules-5.8.7-5ubuntu1.2 (Ubuntu 5.10) - perl-suid-5.8.7-5ubuntu1.2 (Ubuntu 5.10) Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: Ubuntu Security Notice (C) 2005 Canonical, Inc. / NASL script (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

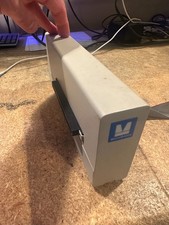
Microbotics Starboard 2MB + SCSI Sidecar for Amiga 1000 Vintage Computer READ
$329.00
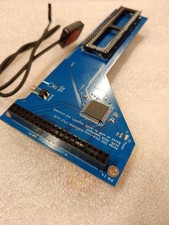
RGB2HDMI Amiga 500 UltraLong (Accelerator Friendly) HDMI Games, non-RTG A500
$50.00
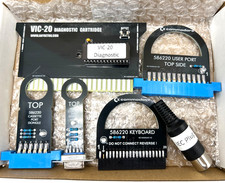
Commodore VIC-20 Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
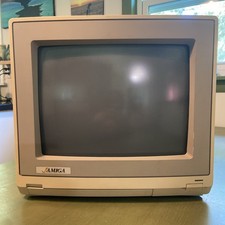
Amiga Model 1080 RGB color CRT monitor - Parts Or Repair - Doesn’t Power On
$100.00
Amiga Emplant Emulator Card For Commodore Amiga 2000 4000 3000
$249.00
HighFlyer Amiga 4000 Tower & Bus Extender, Expansion Systems A4000T Kit
$888.50
Commodore Amiga 4000 Motherboard Rev B - untested
$225.00
BlueSCSI v2 Internal 50-pin 3.5" SCSI Drive ,Wi-Fi,For Macintosh, Amiga, PC
$52.99
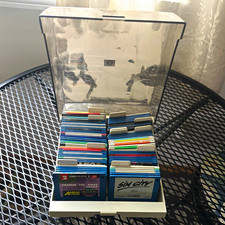
ALS Storage Box with Assorted Amiga Format 3.5" Floppy Disks
$199.00
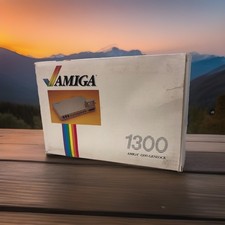
OPEN BOX - AMIGA Genlock Interface Vintage Video Adapter 1300- GREAT
$329.95
|
||
|
No Discussions have been posted on this vulnerability. |