|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Ubuntu Local Security Checks >> USN149-1 : mozilla-firefox vulnerabilities Vulnerability Assessment Details
|
USN149-1 : mozilla-firefox vulnerabilities |
||
|
mozilla-firefox vulnerabilities Detailed Explanation for this Vulnerability Assessment Summary : These remote packages are missing security patches : - mozilla-firefox - mozilla-firefox-dev - mozilla-firefox-dom-inspector - mozilla-firefox-gnome-support Description : Secunia.com reported that one of the recent security patches in Firefox reintroduced the frame injection patch that was originally known as CVE-2004-0718. This permited a malicious web site to spoof the contents of other web sites. (CVE-2005-1937) In several places the browser user interface did not correctly distinguish between true user events, such as mouse clicks or keystrokes, and synthetic events genenerated by web content. This could be exploited by malicious web sites to generate e. g. mouse clicks that install malicious tests. Synthetic events are now prevented from reaching the browser UI entirely. (CVE-2005-2260) Scripts in XBL controls from web content continued to be run even when Javascript was disabled. This could be combined with most script-based exploits to attack people running vulnerable versions who thought disabling Javascript would protect them. (CVE-2005-2261) Matthew Mastracci discovered a flaw in the addons installation launcher. By forcing a page navigation immediately after ca [...] Solution : Upgrade to : - mozilla-firefox-1.0.2-0ubuntu5.4 (Ubuntu 5.04) - mozilla-firefox-dev-1.0.2-0ubuntu5.4 (Ubuntu 5.04) - mozilla-firefox-dom-inspector-1.0.2-0ubuntu5.4 (Ubuntu 5.04) - mozilla-firefox-gnome-support-1.0.2-0ubuntu5.4 (Ubuntu 5.04) Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: Ubuntu Security Notice (C) 2005 Canonical, Inc. / NASL script (C) 2005 Michel Arboi |
||
|
Cables, Connectors |


Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00
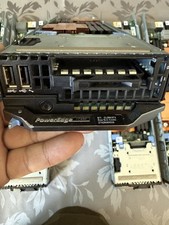
Dell PowerEdge FC430 Blade Server 2x Xeon E5-2630v4 20 Cores FX2 FX2s No RAM/HDD
$119.99
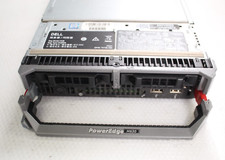
Dell PowerEdge M630 Blade Server 2x Xeon E5-2680 v4, 2F3MP , 4GDP5 ,R10KJ ,JVFVR
$95.20
Dell PowerEdge M620 Blade Server 2x Xeon E5-2680v2 2.8ghz 20-Cores | 128GB
$149.99
NETAPP HCI NAF-1701 SuperMicro Server 4X BLADE H410C 8X GOLD 5120 4 NODE SERVER
$1499.97
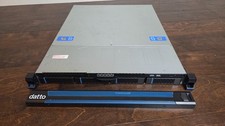
Datto S4P10 1U Blade Rack Server Intel Xeon D-2143IT 2.20GHz 48GB DDR4 4-Bay PSU
$229.95
Dell Poweredge C6400 24x 2.5’’ 2x 2400W 4x C6420 Nodes H330 | 2x SFP | 8x Trays
$799.99
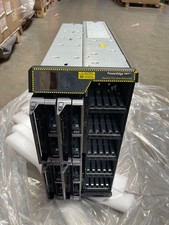
Dell PowerEdge VRTX 2.5"x25 Bay Blade Enclosure 4x1600W + 4X M640 (4X Blades)
$1599.99
Dell PowerEdge M640 Blade Barebone Server Dell P/N: HHB006 Tested Working
$149.99
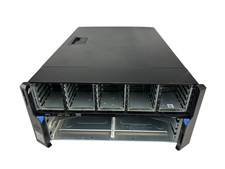
Dell Poweredge VRTX 25Bay 2.5" 2x PERC 8, 2xCMC, I/O 1GB Pass Through, 4x PS
$578.08
|
||
|
No Discussions have been posted on this vulnerability. |