|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0199: mozilla Vulnerability Assessment Details
|
RHSA-2006-0199: mozilla |
||
|
Check for the version of the mozilla packages Detailed Explanation for this Vulnerability Assessment Updated mozilla packages that fix several security bugs are now available. This update has been rated as having critical security impact by the Red Hat Security Response Team. Mozilla is an open source Web browser, advanced email and newsgroup client, IRC chat client, and HTML editor. Igor Bukanov discovered a bug in the way Mozilla's Javascript interpreter dereferences objects. If a user visits a malicious web page, Mozilla could crash or execute arbitrary code as the user running Mozilla. The Common Vulnerabilities and Exposures project assigned the name CVE-2006-0292 to this issue. moz_bug_r_a4 discovered a bug in Mozilla's XULDocument.persist() function. A malicious web page could inject arbitrary RDF data into a user's localstore.rdf file, which can cause Mozilla to execute arbitrary javascript when a user runs Mozilla. (CVE-2006-0296) A denial of service bug was found in the way Mozilla saves history information. If a user visits a web page with a very long title, it is possible Mozilla will crash or take a very long time the next time it is run. (CVE-2005-4134) Note that the Red Hat Enterprise Linux 3 packages also fix a bug when using XSLT to transform documents. Passing DOM Nodes as parameters to functions expecting an xsl:param could cause Mozilla to throw an exception. Users of Mozilla are advised to upgrade to these updated packages, which contain backported patches to correct these issues. Solution : http://rhn.redhat.com/errata/RHSA-2006-0199.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

Microbotics Starboard 2MB + SCSI Sidecar for Amiga 1000 Vintage Computer READ
$329.00
RGB2HDMI Amiga 500 UltraLong (Accelerator Friendly) HDMI Games, non-RTG A500
$50.00
Commodore VIC-20 Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
Amiga Model 1080 RGB color CRT monitor - Parts Or Repair - Doesn’t Power On
$100.00
Amiga Emplant Emulator Card For Commodore Amiga 2000 4000 3000
$249.00
Commodore Amiga 4000 Motherboard Rev B - untested
$225.00
HighFlyer Amiga 4000 Tower & Bus Extender, Expansion Systems A4000T Kit
$888.50
BlueSCSI v2 Internal 50-pin 3.5" SCSI Drive ,Wi-Fi,For Macintosh, Amiga, PC
$52.99
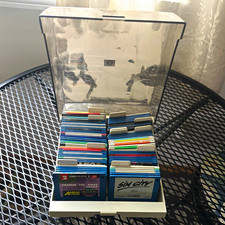
ALS Storage Box with Assorted Amiga Format 3.5" Floppy Disks
$199.00
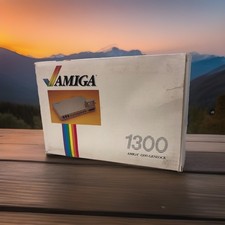
OPEN BOX - AMIGA Genlock Interface Vintage Video Adapter 1300- GREAT
$329.95
|
||
|
No Discussions have been posted on this vulnerability. |