|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0140: kernel Vulnerability Assessment Details
|
RHSA-2006-0140: kernel |
||
|
Check for the version of the kernel packages Detailed Explanation for this Vulnerability Assessment Updated kernel packages that fix several security issues in the Red Hat Enterprise Linux 3 kernel are now available. This security advisory has been rated as having important security impact by the Red Hat Security Response Team. The Linux kernel handles the basic functions of the operating system. These new kernel packages contain fixes for the security issues described below: - a flaw in network IGMP processing that a permited a remote user on the local network to cause a denial of service (disabling of multicast reports) if the system is running multicast applications (CVE-2002-2185, moderate) - a flaw in remap_page_range() with O_DIRECT writes that permited a local user to cause a denial of service (crash) (CVE-2004-1057, important) - a flaw in exec() handling on some 64-bit architectures that permited a local user to cause a denial of service (crash) (CVE-2005-2708, important) - a flaw in procfs handling during unloading of modules that permited a local user to cause a denial of service or potentially gain rights (CVE-2005-2709, moderate) - a flaw in IPv6 network UDP port hash table lookups that permited a local user to cause a denial of service (hang) (CVE-2005-2973, important) - a flaw in 32-bit-compat handling of the TIOCGDEV ioctl that permited a local user to cause a denial of service (crash) (CVE-2005-3044, important) - a network buffer info leak using the orinoco driver that permited a remote user to possibly view uninitialized data (CVE-2005-3180, important) - a flaw in IPv4 network TCP and UDP netfilter handling that permited a local user to cause a denial of service (crash) (CVE-2005-3275, important) - a flaw in the IPv6 flowlabel code that permited a local user to cause a denial of service (crash) (CVE-2005-3806, important) - a flaw in network ICMP processing that permited a local user to cause a denial of service (memory exhaustion) (CVE-2005-3848, important) - a flaw in file lease time-out handling that permited a local user to cause a denial of service (log file overflow) (CVE-2005-3857, moderate) - a flaw in network IPv6 xfrm handling that permited a local user to cause a denial of service (memory exhaustion) (CVE-2005-3858, important) All Red Hat Enterprise Linux 3 users are advised to upgrade their kernels to the packages associated with their machine architecture and configurations as listed in this erratum. Solution : http://rhn.redhat.com/errata/RHSA-2006-0140.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

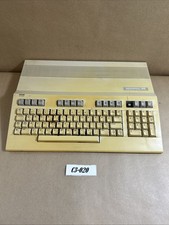
Commodore 128 C128 Computer FOR PARTS / REPAIR Untested Missing Key No Cords
$149.99
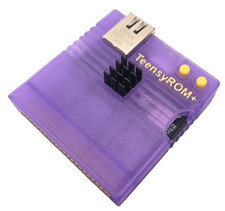
TeensyROM+ TR+ v0.4 Cartridge for C64/128 - w/ Case & 32GB SD Preloaded
$89.50
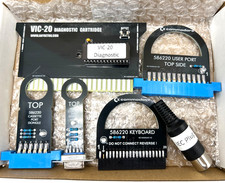
Commodore VIC-20 Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
RARE Commodore MPS801 Printer - 1st printer for the 64 - powers on
$70.00
Commodore 64 Serial Cable 6PIN DIN 1541 1571 C64 128 C128 Disk Drive Printer USA
$10.49
Commodore 1541 Emulator PI1541 HAT with ROTARY, OLED screen, USA Seller
$29.99
Vtg 128 / 64 Commodore 1541-II Computer Disk Drive in Box 5.25 Floppy (Working)
$89.99
Commodore 64 PC with Model 1541 Diskette Drive and Flight Simulator II *READ*
$199.99
Commodore 64 Dead Test & Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
Commodore 64 Drive Alignment & Utility Diskette
$9.99
|
||
|
No Discussions have been posted on this vulnerability. |