|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2004-017: kernel Vulnerability Assessment Details
|
RHSA-2004-017: kernel |
||
|
Check for the version of the kernel packages Detailed Explanation for this Vulnerability Assessment Updated kernel packages are now available as part of ongoing support and maintenance of Red Hat Enterprise Linux version 3. This is the first regular update. The Linux kernel handles the basic functions of the operating system. This is the first regular kernel update for Red Hat Enterprise Linux version 3. It contains a new critical security fix, many other bug fixes, several device driver updates, and numerous performance and scalability enhancements. On AMD64 systems, a fix was made to the eflags checking in 32-bit ptrace emulation that could have permited local users to elevate their rights. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0001 to this issue. Other bug fixes were made in the following kernel areas: VM, NPTL, IPC, kernel timer, ext3, NFS, netdump, SCSI, ACPI, several device drivers, and machine-dependent support for the x86_64, ppc64, and s390 architectures. The VM subsystem was improved to better handle extreme loads and resource contention (such as might occur during heavy database application usage). This has resulted in a significantly reduced possibility of hangs, OOM kills, and low-mem exhaustion. Several NPTL fixes were made to resolve POSIX compliance issues concerning process IDs and thread IDs. A section in the Release Notes elaborates on a related issue with file record locking in multi-threaded applications. AMD64 kernels are now configured with NUMA support, S390 kernels now have CONFIG_BLK_STATS enabled, and DMA capability was restored in the IA64 agpgart driver. The following drivers have been upgraded to new versions: cmpci ------ 6.36 e100 ------- 2.3.30-k1 e1000 ------ 5.2.20-k1 ips -------- 6.10.52 megaraid --- v1.18k megaraid2 -- v2.00.9 All Red Hat Enterprise Linux 3 users are advised to upgrade their kernels to the packages associated with their machine architectures and configurations as listed in this erratum. Solution : http://rhn.redhat.com/errata/RHSA-2004-017.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

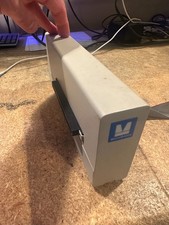
Microbotics Starboard 2MB + SCSI Sidecar for Amiga 1000 Vintage Computer READ
$329.00
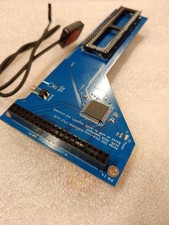
RGB2HDMI Amiga 500 UltraLong (Accelerator Friendly) HDMI Games, non-RTG A500
$50.00
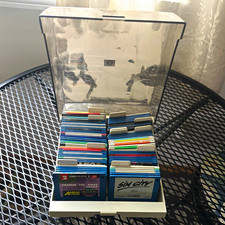
ALS Storage Box with Assorted Amiga Format 3.5" Floppy Disks
$199.00
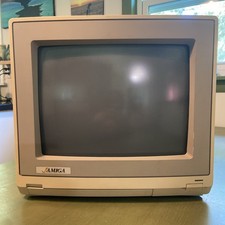
Amiga Model 1080 RGB color CRT monitor - Parts Or Repair - Doesn’t Power On
$100.00
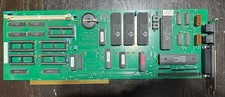
Amiga Emplant Emulator Card For Commodore Amiga 2000 4000 3000
$249.00
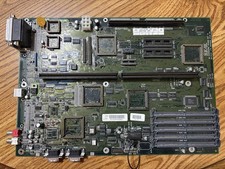
Commodore Amiga 4000 Motherboard Rev B - untested
$225.00
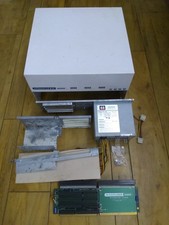
HighFlyer Amiga 4000 Tower & Bus Extender, Expansion Systems A4000T Kit
$888.50
BlueSCSI v2 Internal 50-pin 3.5" SCSI Drive ,Wi-Fi,For Macintosh, Amiga, PC
$52.99
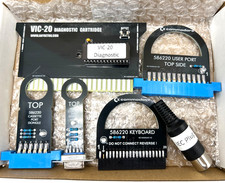
Commodore VIC-20 Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
OPEN BOX - AMIGA Genlock Interface Vintage Video Adapter 1300- GREAT
$329.95
|
||
|
No Discussions have been posted on this vulnerability. |