|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2002-227: kernel Vulnerability Assessment Details
|
RHSA-2002-227: kernel |
||
|
Check for the version of the kernel packages Detailed Explanation for this Vulnerability Assessment This kernel update for Red Hat Linux Advanced Server 2.1 addresses some security issues and provides minor bug fixes. The Linux kernel handles the basic functions of the operating system. A number of vulnerabilities were found in the Red Hat Linux Advanced Server kernel. These vulnerabilities could permit a local user to obtain elevated (root) rights. The vulnerabilities existed in a number of drivers, including stradis, rio500, se401, apm, usbserial, and usbvideo. Additionally, a number of bugs have been fixed, and some small feature enhancements have been added. - Failed READA requests could be interpreted as I/O errors under high load on SMP this has been fixed. - In rare cases, TLB entries could be corrupted on SMP Pentium IV systems this potential for corruption has been fixed. Third-party modules will need to be recompiled to take advantage of these fixes. - The latest tg3 driver fixes have been included the tg3 driver now supports more hardware. - A mechanism is provided to specify the location of core files and to set the name pattern to include the UID, program, hostname, and PID of the process that caused the core dump. A number of SCSI fixes have also been included: - Configure sparse LUNs in the qla2200 driver - Clean up erroneous accounting data as seen by /proc/partitions and iostat - Allow up to 128 scsi disks - Do not start logical units that require manual intervention, avoiding unnecessary startup delays - Improve SCSI layer throughput by properly clustering DMA requests All users of Red Hat Linux Advanced Server are advised to upgrade to the errata packages. Solution : http://rhn.redhat.com/errata/RHSA-2002-227.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

🔀 Juniper Networks EX2300-C-12P 12× Gigabit PoE+ • 2× 10G SFP+ Compact Switch ⚡
$109.99
Juniper EX2300 12-Port Gigabit PoE+ Managed Network Switch P/N: EX2300-C-12P
$149.99
Juniper EX3400-24P 24-Port PoE+ GbE + 4-Port 1/10Gb SFP Switch
$245.00
Juniper Networks Mist Wireless Access Points, Model AP45
$59.99
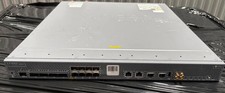
Juniper MX204 +JUNOS and Dual Power Supply
$7299.99
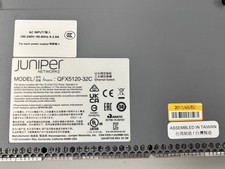
Juniper Networks QFX5120-32C Ethernet Switch, Server Component
$5999.95
Juniper Networks MX204-HW-BASE *BRAND NEW FACTORY SEALED* READ DETAILS
$8199.99
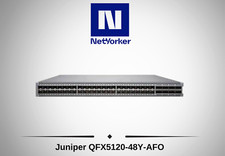
Juniper QFX5120-48Y-AFO 48 x 1/10/25GB SFP28 + 8 x 40/100GB Switch w/Dual AC
$10499.99
Juniper EX4300-24P 24 Port Gigabit PoE+ Switch.
$95.55
Juniper Networks EX3400-24T 24-Port Ethernet Switch w/Power Cord
$174.99
|
||
|
No Discussions have been posted on this vulnerability. |