|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2006:172-1: openssl Vulnerability Assessment Details
|
MDKSA-2006:172-1: openssl |
||
|
Check for the version of the openssl package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2006:172-1 (openssl). Dr S N Henson of the OpenSSL core team and Open Network Security recently developed an ASN1 test suite for NISCC (www.niscc.gov.uk). When the test suite was run against OpenSSL two denial of service vulnerabilities were discovered. During the parsing of certain invalid ASN1 structures an error condition is mishandled. This can result in an infinite loop which consumes system memory. (CVE-2006-2937) Certain types of public key can take disproportionate amounts of time to process. This could be used by a possible hacker in a denial of service attack. (CVE-2006-2940) Tavis Ormandy and Will Drewry of the Google Security Team discovered a buffer overflow in the SSL_get_shared_ciphers utility function, used by some applications such as exim and mysql. A possible hacker could send a list of ciphers that would overrun a buffer. (CVE-2006-3738) Tavis Ormandy and Will Drewry of the Google Security Team discovered a possible DoS in the sslv2 client code. Where a client application uses OpenSSL to make a SSLv2 connection to a malicious server that server could cause the client to crash. (CVE-2006-4343) Updated packages are patched to address these issues. Update: There was an error in the original published patches for CVE-2006-2940. New packages have corrected this issue. Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2006:172-1 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2007 Tenable Network Security |
||
|
Cables, Connectors |

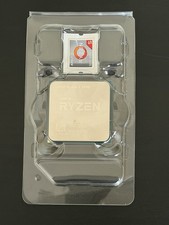
AMD Ryzen 5 5500 Processor ( read Description)
$59.00
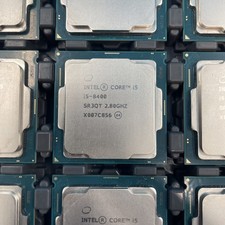
(LOT OF 20) Intel Core i5-8400 CPU 2.80GHz Desktop Processor (SR3QT)
$700.00
INTEL CORE I9-10940X X-SERIES PROCESSOR | 3.30GHZ | SRGSH
$179.99
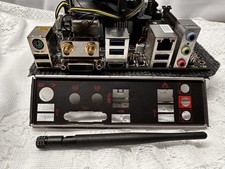
Compo MSI B150I GAMING PRO AC LGA1151 16 Gb DDR4 + Cpu I7 6700+I/O Shields.
$159.00
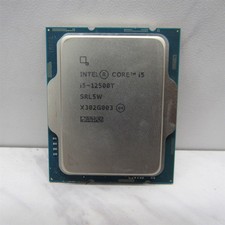
Intel Core i5-12500T SRL5W 2GHz 18MB 6 Core Socket LGA1700 Desktop CPU Processor
$114.99
Intel Core i7-9700 Octa-Core 3 GHz Desktop Processor LGA 1151
$79.99
Intel Core i7-3770K 3.5 GHz Processor
$39.00
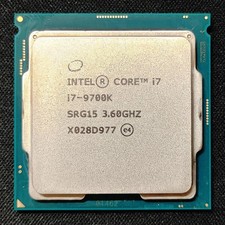
Intel Core i7-9700K Octa-Core 3.6 GHz Desktop CPU
$99.99
Intel Core i7-4770 3.40GHz Quad Core SR149 LGA 1150 CPU Processor tested
$35.00
Intel Core i7-11700K 3.60GHz 11th Gen CPU Processor MPN SRKNL X239G085
$140.00
|
||
|
No Discussions have been posted on this vulnerability. |