|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2006:098: postgresql Vulnerability Assessment Details
|
MDKSA-2006:098: postgresql |
||
|
Check for the version of the postgresql package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2006:098 (postgresql). PostgreSQL 8.1.x before 8.1.4, 8.0.x before 8.0.8, 7.4.x before 7.4.13, 7.3.x before 7.3.15, and earlier versions permits context-dependent attackers to bypass SQL injection protection methods in applications via invalid encodings of multibyte characters, aka one variant of 'Encoding-Based SQL Injection.' (CVE-2006-2313) PostgreSQL 8.1.x before 8.1.4, 8.0.x before 8.0.8, 7.4.x before 7.4.13, 7.3.x before 7.3.15, and earlier versions permits context-dependent attackers to bypass SQL injection protection methods in applications that use multibyte encodings that permit the '' (backslash) byte 0x5c to be the trailing byte of a multibyte character, such as SJIS, BIG5, GBK, GB18030, and UHC, which cannot be handled correctly by a client that does not understand multibyte encodings, aka a second variant of 'Encoding-Based SQL Injection.' NOTE: it could be argued that this is a class of issue related to interaction errors between the client and PostgreSQL, but a CVE has been assigned since PostgreSQL is treating this as a preventative measure against this class of problem. (CVE-2006-2314) Packages have been patched or updated to correct these issues. Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2006:098 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

Commodore 128 C128 Computer FOR PARTS / REPAIR Untested Missing Key No Cords
$149.99
TeensyROM+ TR+ v0.4 Cartridge for C64/128 - w/ Case & 32GB SD Preloaded
$89.50
Commodore VIC-20 Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
RARE Commodore MPS801 Printer - 1st printer for the 64 - powers on
$70.00
Commodore 1750 512K RAM Expansion REU for C128 / C64 – Tested & Working
$110.00
Commodore 64 Serial Cable 6PIN DIN 1541 1571 C64 128 C128 Disk Drive Printer USA
$10.49
Commodore 1541 Emulator PI1541 HAT with ROTARY, OLED screen, USA Seller
$29.99
Vtg 128 / 64 Commodore 1541-II Computer Disk Drive in Box 5.25 Floppy (Working)
$89.99
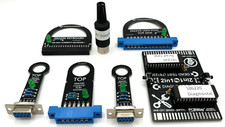
Commodore 64 Dead Test & Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
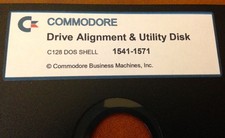
Commodore 64 Drive Alignment & Utility Diskette
$9.99
|
||
|
No Discussions have been posted on this vulnerability. |