|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Settings >> HTTP NIDS evasion Vulnerability Assessment Details
|
HTTP NIDS evasion |
||
|
NIDS evasion options Detailed Explanation for this Vulnerability Assessment This test configures Nessus for NIDS evasion (see the 'Prefs' panel). NIDS evasion options are useful if you want to acertain the quality of the expensive NIDS you just bought. HTTP evasion techniques : - HEAD: use HEAD method instead of GET - URL encoding: - Hex: change characters to %XX - MS UTF-16: change characters to %uXXXX. This works only with IIS. - UTF-16: change characters to %00%XX. This should *not* work! - Broken UTF-8: change characters to invalid multibyte UTF8 sequences. - Absolute URI: insert scheme://host/ in front of the relative URI. - Double slashes: change every / to // - Reverse traversal: change / into /dirname/../ 'Basic' inserts 8 characters random directory names 'Long' means 1000 character directory name. - Self-reference: changes every / to /./ - Premature request ending: just like 'reverse traversal', but the directory name contains %0d%0a (could be translated to CR LF) - CGI.pm: uses ' ' instead of '&' in the query string. - Parameter hiding: another form of reverse traversal. The directory contains %3F (could be translated to ?) - Dos/Windows: uses \ instead of / - Null method: insert %00 between the method and the URI - TAB: uses TAB instead of SPACE between the method, the URL and the HTTP version - HTTP/0.9: uses HTTP/0.9 requests (method & URI only, no HTTP version field) 'Premature request ending' and 'Parameter hiding' target 'smart' IDS. Read http://www.wiretrip.net/rfp/pages/whitepapers/whiskerids.html for more information. Warning: those features are experimental and some options may result in false negatives! This test does not do any security check. Network Security Threat Level: None Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2002 Michel Arboi / Renaud Deraison |
||
|
Cables, Connectors |

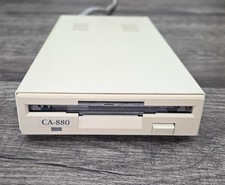
💾 External Floppy Drive for Commodore Amiga, California Access CA-880
$89.00
Microbotics Starboard 2MB + SCSI Sidecar for Amiga 1000 Vintage Computer READ
$329.00
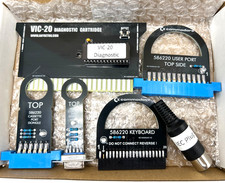
Commodore VIC-20 Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
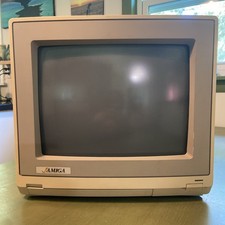
Amiga Model 1080 RGB color CRT monitor - Parts Or Repair - Doesn’t Power On
$100.00
Amiga Emplant Emulator Card For Commodore Amiga 2000 4000 3000
$249.00
Commodore Amiga 4000 Motherboard Rev B - untested
$225.00
HighFlyer Amiga 4000 Tower & Bus Extender, Expansion Systems A4000T Kit
$888.50
BlueSCSI v2 Internal 50-pin 3.5" SCSI Drive ,Wi-Fi,For Macintosh, Amiga, PC
$52.99
RGB2HDMI Amiga 500 UltraLong (Accelerator Friendly) HDMI Games, non-RTG A500
$50.00
ALS Storage Box with Assorted Amiga Format 3.5" Floppy Disks
$199.00
|
||
|
No Discussions have been posted on this vulnerability. |