|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SMTP problems >> HELO overflow Vulnerability Assessment Details
|
HELO overflow |
||
|
Checks if the remote mail server can be used to send anonymous mail Detailed Explanation for this Vulnerability Assessment The remote SMTP server seems to permit remote users to send mail anonymously by providing arguments that are too long to the HELO command (more than 1024 chars). This problem may permit malicious users to send hate mail or threatening mail using your server, and keep their anonymity. Network Security Threat Level: Low Solution : If you are using sendmail, upgrade to version 8.9.x or newer. If you do not run sendmail, contact your vendor. Networks Security ID: 61, 62 Vulnerability Assessment Copyright: This script is Copyright (C) 1999 Renaud Deraison |
||
|
Cables, Connectors |

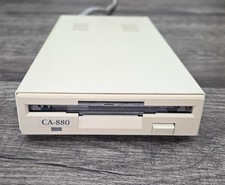
💾 External Floppy Drive for Commodore Amiga, California Access CA-880
$89.00
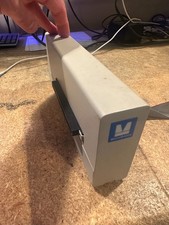
Microbotics Starboard 2MB + SCSI Sidecar for Amiga 1000 Vintage Computer READ
$329.00
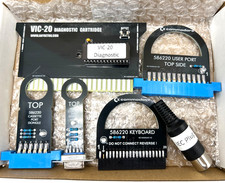
Commodore VIC-20 Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
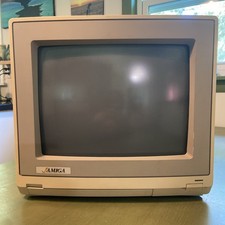
Amiga Model 1080 RGB color CRT monitor - Parts Or Repair - Doesn’t Power On
$100.00
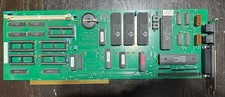
Amiga Emplant Emulator Card For Commodore Amiga 2000 4000 3000
$249.00
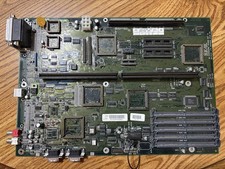
Commodore Amiga 4000 Motherboard Rev B - untested
$225.00
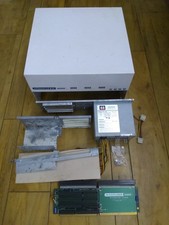
HighFlyer Amiga 4000 Tower & Bus Extender, Expansion Systems A4000T Kit
$888.50
BlueSCSI v2 Internal 50-pin 3.5" SCSI Drive ,Wi-Fi,For Macintosh, Amiga, PC
$52.99
RGB2HDMI Amiga 500 UltraLong (Accelerator Friendly) HDMI Games, non-RTG A500
$50.00
ALS Storage Box with Assorted Amiga Format 3.5" Floppy Disks
$199.00
|
||
|
No Discussions have been posted on this vulnerability. |