|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200612-06] Mozilla Thunderbird: Multiple vulnerabilities Vulnerability Assessment Details
|
[GLSA-200612-06] Mozilla Thunderbird: Multiple vulnerabilities |
||
|
Mozilla Thunderbird: Multiple vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200612-06 (Mozilla Thunderbird: Multiple vulnerabilities) It has been identified that Mozilla Thunderbird improperly handles Script objects while they are being executed, permiting them to be modified during execution. JavaScript is disabled in Mozilla Thunderbird by default. Mozilla Thunderbird has also been found to be vulnerable to various potential buffer overflows. Lastly, the binary release of Mozilla Thunderbird is vulnerable to a low exponent RSA signature forgery issue because it is bundled with a vulnerable version of NSS. Impact A possible hacker could entice a user to view a specially crafted email that causes a buffer overflow and again executes arbitrary code or causes a Denial of Service. A possible hacker could also entice a user to view an email containing specially crafted JavaScript and execute arbitrary code with the rights of the user running Mozilla Thunderbird. It is important to note that JavaScript is off by default in Mozilla Thunderbird, and enabling it is strongly discouraged. It is also possible for a possible hacker to create SSL/TLS or email certificates that would not be detected as invalid by the binary release of Mozilla Thunderbird, raising the possibility for Man-in-the-Middle attacks. Workaround There is no known workaround at this time. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-5462 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-5463 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-5464 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-5747 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-5748 https://bugzilla.mozilla.org/show_bug.cgi?id=360409 Solution: Users upgrading to the following releases of Mozilla Thunderbird should note that this version of Mozilla Thunderbird has been found to not display certain messages in some cases. All Mozilla Thunderbird users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=mail-client/mozilla-thunderbird-1.5.0.8" All Mozilla Thunderbird binary release users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=mail-client/mozilla-thunderbird-bin-1.5.0.8" Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: (C) 2006 Michel Arboi |
||
|
Cables, Connectors |

Novell SUSE Linux Enterprise Server 9, Linux Professional 8.2 / 9.1 — 3 DVD Set
$58.00
Ubuntu Server 26.04.1 LTS Bootable USB Flash Drive – Latest September 2026
$12.99
OPNsense pfSense 8-Core Atom C3758 2.2GHz 8GB DDR4 64GB SSD 8x NIC QAT AES VPN
$115.00
RED HAT ENTERPRISE LINUX 5 SERVER RHF0382US-R1 for PC x86 AMD 64 INTEL 64 30 Day
$188.24
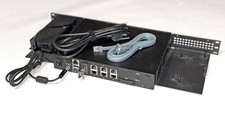
OPNsense Firewall VPN QAT 8-Core Atom C3758 2.20GHz 16GB DDR4 128GB SSD 8xNIC
$175.00
All New Ubuntu 26.04 LTS Linux Bootable USB Flash Drive
$15.95
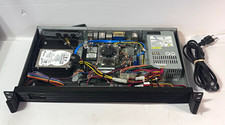
1U Rackmount PC Intel Core i5-2520M 8GB RAM 500GB HDD Ubuntu Linux Server
$109.99
Microsoft SQL Server 2019 Enterprise 40 Core Unlimited CAL Retail License FPP
$299.00
SQL Server 2022 Enterprise 96 Core License & DVD Unlimited CALs with CoA
$284.99
Sun Enterprise e450 400mhz cpu(x4), 4gb ram, 9gb HD w/spud most complete on ebay
$500.00
|
||
|
No Discussions have been posted on this vulnerability. |