|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200412-16] kdelibs, kdebase: Multiple vulnerabilities Vulnerability Assessment Details
|
[GLSA-200412-16] kdelibs, kdebase: Multiple vulnerabilities |
||
|
kdelibs, kdebase: Multiple vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200412-16 (kdelibs, kdebase: Multiple vulnerabilities) Daniel Fabian discovered that the KDE core libraries contain a flaw permiting password disclosure by making a link to a remote file. When creating this link, the resulting URL contains authentication credentials used to access the remote file (CAN 2004-1171). The Konqueror webbrowser permits websites to load webpages into a window or tab currently used by another website (CVE-2004-1158). Impact A malicious user could have access to the authentication credentials of other users depending on the file permissions. A malicious website could use the window injection vulnerability to load content in a window apparently belonging to another website. Workaround There is no known workaround at this time. References: http://www.kde.org/info/security/advisory-20041209-1.txt http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-1171 http://www.kde.org/info/security/advisory-20041213-1.txt http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-1158 Solution: All kdelibs users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=kde-base/kdelibs-3.2.3-r4" All kdebase users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=kde-base/kdebase-3.2.3-r3" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

Commodore 128 C128 Computer FOR PARTS / REPAIR Untested Missing Key No Cords
$149.99
TeensyROM+ TR+ v0.4 Cartridge for C64/128 - w/ Case & 32GB SD Preloaded
$89.50
Commodore VIC-20 Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
RARE Commodore MPS801 Printer - 1st printer for the 64 - powers on
$70.00
Commodore 64 Serial Cable 6PIN DIN 1541 1571 C64 128 C128 Disk Drive Printer USA
$10.49
Commodore 1541 Emulator PI1541 HAT with ROTARY, OLED screen, USA Seller
$29.99
Vtg 128 / 64 Commodore 1541-II Computer Disk Drive in Box 5.25 Floppy (Working)
$89.99
Commodore 64 PC with Model 1541 Diskette Drive and Flight Simulator II *READ*
$199.99
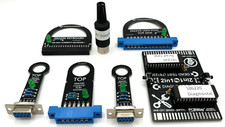
Commodore 64 Dead Test & Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
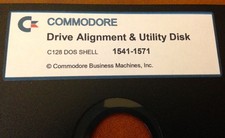
Commodore 64 Drive Alignment & Utility Diskette
$9.99
|
||
|
No Discussions have been posted on this vulnerability. |