|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200403-11] Squid ACL [url_regex] bypass vulnerability Vulnerability Assessment Details
|
[GLSA-200403-11] Squid ACL [url_regex] bypass vulnerability |
||
|
Squid ACL [url_regex] bypass vulnerability Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200403-11 (Squid ACL [url_regex] bypass vulnerability) A bug in Squid permits users to bypass certain access controls by passing a URL containing "%00" which exploits the Squid decoding function. This may insert a NUL character into decoded URLs, which may permit users to bypass url_regex access control lists that are enforced upon them. In such a scenario, Squid will insert a NUL character after the"%00" and it will make a comparison between the URL to the end of the NUL character rather than the contents after it: the comparison does not result in a match, and the user's request is not denied. Impact Restricted users may be able to bypass url_regex access control lists that are enforced upon them which may cause unwanted network traffic as well as a route for other possible exploits. Users of Squid 2.5STABLE4 and below who require the url_regex features are recommended to upgrade to 2.5STABLE5 to maintain the security of their infrastructure. Workaround A workaround is not currently known for this issue. All users are advised to upgrade to the latest version of Squid. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0189 http://www.squid-cache.org/Advisories/SQUID-2004_1.txt Solution: Squid can be updated as follows: # emerge sync # emerge -pv ">=www-proxy/squid-2.5.5" # emerge ">=www-proxy/squid-2.5.5" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

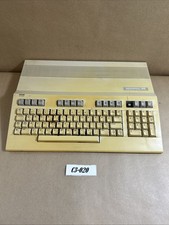
Commodore 128 C128 Computer FOR PARTS / REPAIR Untested Missing Key No Cords
$149.99
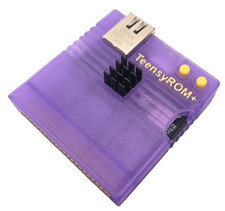
TeensyROM+ TR+ v0.4 Cartridge for C64/128 - w/ Case & 32GB SD Preloaded
$89.50
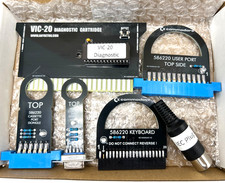
Commodore VIC-20 Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
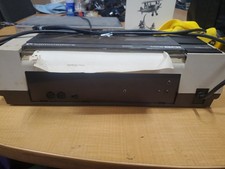
RARE Commodore MPS801 Printer - 1st printer for the 64 - powers on
$70.00
Commodore 64 Serial Cable 6PIN DIN 1541 1571 C64 128 C128 Disk Drive Printer USA
$10.49
Commodore 1541 Emulator PI1541 HAT with ROTARY, OLED screen, USA Seller
$29.99
Vtg 128 / 64 Commodore 1541-II Computer Disk Drive in Box 5.25 Floppy (Working)
$89.99
Commodore 64 PC with Model 1541 Diskette Drive and Flight Simulator II *READ*
$199.99
Commodore 64 Dead Test & Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
Commodore 64 Drive Alignment & Utility Diskette
$9.99
|
||
|
No Discussions have been posted on this vulnerability. |