|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200402-01] PHP setting leaks from .htaccess files on virtual hosts Vulnerability Assessment Details
|
[GLSA-200402-01] PHP setting leaks from .htaccess files on virtual hosts |
||
|
PHP setting leaks from .htaccess files on virtual hosts Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200402-01 (PHP setting leaks from .htaccess files on virtual hosts) If the server configuration "php.ini" file has "register_globals = on" and a request is made to one virtual host (which has "php_admin_flag register_globals off") and the next request is sent to the another virtual host (which does not have the setting) through the same apache child, the setting will persist. Impact Depending on the server and site, a possible hacker may be able to exploit global variables to gain access to reserved areas, such as MySQL passwords, or this vulnerability may simply cause a lack of functionality. As a result, users are urged to upgrade their PHP installations. Gentoo ships PHP with "register_globals" set to "off" by default. This issue affects both servers running Apache 1.x and servers running Apache 2.x. Workaround No immediate workaround is available a software upgrade is required. References: http://bugs.php.net/bug.php?id=25753 Solution: All users are recommended to upgrade their PHP installation to 4.3.4-r4: # emerge sync # emerge -pv ">=dev-php/mod_php-4.3.4-r4" # emerge ">=dev-php/mod_php-4.3.4-r4" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

Novell SUSE Linux Enterprise Server 9, Linux Professional 8.2 / 9.1 — 3 DVD Set
$58.00
Ubuntu Server 26.04.1 LTS Bootable USB Flash Drive – Latest September 2026
$12.99
OPNsense pfSense 8-Core Atom C3758 2.2GHz 8GB DDR4 64GB SSD 8x NIC QAT AES VPN
$115.00
RED HAT ENTERPRISE LINUX 5 SERVER RHF0382US-R1 for PC x86 AMD 64 INTEL 64 30 Day
$188.24
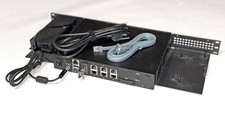
OPNsense Firewall VPN QAT 8-Core Atom C3758 2.20GHz 16GB DDR4 128GB SSD 8xNIC
$175.00
All New Ubuntu 26.04 LTS Linux Bootable USB Flash Drive
$15.95
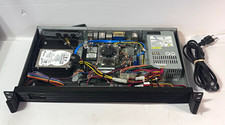
1U Rackmount PC Intel Core i5-2520M 8GB RAM 500GB HDD Ubuntu Linux Server
$109.99
Microsoft SQL Server 2019 Enterprise 40 Core Unlimited CAL Retail License FPP
$299.00
SQL Server 2022 Enterprise 96 Core License & DVD Unlimited CALs with CoA
$284.99
Sun Enterprise e450 400mhz cpu(x4), 4gb ram, 9gb HD w/spud most complete on ebay
$500.00
|
||
|
No Discussions have been posted on this vulnerability. |