|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 2 2005-241: mailman Vulnerability Assessment Details
|
Fedora Core 2 2005-241: mailman |
||
|
Check for the version of the mailman package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2005-241 (mailman). Mailman is software to help manage email discussion lists, much like Majordomo and Smartmail. Unlike most similar products, Mailman gives each mailing list a webpage, and permits users to subscribe, unsubscribe, etc. over the Web. Even the list manager can administer his or her list entirely from the Web. Mailman also integrates most things people want to do with mailing lists, including archiving, mail < -> news gateways, and so on. Documentation can be found in: /usr/share/doc/mailman-2.1.5 When the package has finished installing, you will need to perform some additional installation steps, these are described in: /usr/share/doc/mailman-2.1.5/INSTALL.REDHAT Update Information: A cross-site scripting (XSS) flaw in the driver script of mailman prior to version 2.1.5 could permit remote attackers to execute scripts as other web users. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-1177 to this issue. Users of mailman should update to this erratum package, which corrects this issue by turning on STEALTH_MODE by default and using Utils.websafe() to quote the html. Solution : http://www.fedoranews.org/blog/index.php?p=511 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

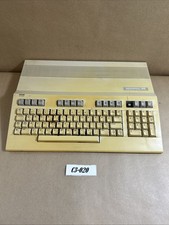
Commodore 128 C128 Computer FOR PARTS / REPAIR Untested Missing Key No Cords
$149.99
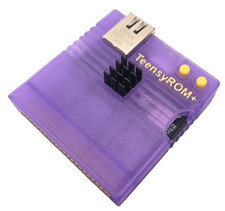
TeensyROM+ TR+ v0.4 Cartridge for C64/128 - w/ Case & 32GB SD Preloaded
$89.50
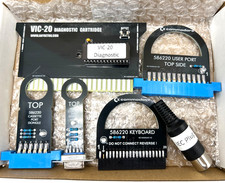
Commodore VIC-20 Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
Commodore OS USB | Bootable LIVE + Install | The Ultimate Gaming Linux OS | NEW
$11.99
Commodore 64 Serial Cable 6PIN DIN 1541 1571 C64 128 C128 Disk Drive Printer USA
$10.49
Commodore 1541 Emulator PI1541 HAT with ROTARY, OLED screen, USA Seller
$29.99
Vtg 128 / 64 Commodore 1541-II Computer Disk Drive in Box 5.25 Floppy (Working)
$89.99
Commodore 64 PC with Model 1541 Diskette Drive and Flight Simulator II *READ*
$199.99
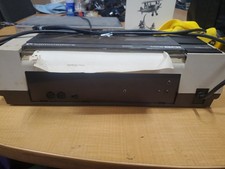
RARE Commodore MPS801 Printer - 1st printer for the 64 - powers on
$70.00
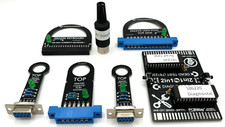
Commodore 64 Dead Test & Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
|
||
|
No Discussions have been posted on this vulnerability. |