|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> CGI abuses >> WebActive world readable log file Vulnerability Assessment Details
|
WebActive world readable log file |
||
|
Requests /active.log Detailed Explanation for this Vulnerability Assessment It is possible to obtain the remote WebActive logfile by requesting the file /active.log A possible hacker may use this to obtain valuable information about your site, such as who visits it and how popular it is. Solution : use another web server, as WebActive is not maintained. If you are using WindowsNT, then remove read access to this file. Network Security Threat Level: Low Networks Security ID: 1497 Vulnerability Assessment Copyright: This script is Copyright (C) 2000 Renaud Deraison |
||
|
Cables, Connectors |

Windows XP, Vista, 8.1, Linux Knoppix, Office XP, (6 CDS)
$10.00
KNOPPIX 9.1 Linux Install & Live DVD 32bit & 64bit
$19.99
KNOPPIX USB DVD OS , BEST OF ALL HIGHLY RECOMENDED
$11.99
Knoppix Live GNU Linux System 9.1 on Bootable CD / DVD / USB Flash Drive
$5.99
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 16G USB Stick
$20.85
$8.00

VINTAGE SOFTWARE | KNOPPIX STD 0.1 (SECURITY TOOLS DISTRIBUTION)
$7.57
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 32G USB Stick
$21.42
$7.00
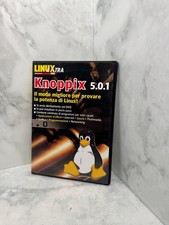
Knoppix 5.0.1 ULTRA RARE Linux DVD - Linux Pro Extra August 2006
$33.98
|
||
|
No Discussions have been posted on this vulnerability. |