|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> CGI abuses >> WEB-INF folder accessible Vulnerability Assessment Details
|
WEB-INF folder accessible |
||
|
Tests for WEB-INF folder access Detailed Explanation for this Vulnerability Assessment This vulnerability affects the Win32 versions of multiple j2ee servlet containers / application servers. By making a particular request to the servers in question it is possible to retrieve files located under the 'WEB-INF' directory. For example: www.someserver.com/WEB-INF./web.xml or www.someserver.com/WEB-INF./classes/MyServlet.class Solution: Contact your vendor for the appropriate patch. Network Security Threat Level: Medium Networks Security ID: 5119 Vulnerability Assessment Copyright: This script is Copyright (C) 2002 Matt Moore |
||
|
Cables, Connectors |

Windows XP, Vista, 8.1, Linux Knoppix, Office XP, (6 CDS)
$10.00
KNOPPIX 9.1 Linux Install & Live DVD 32bit & 64bit
$19.99
KNOPPIX USB DVD OS , BEST OF ALL HIGHLY RECOMENDED
$11.99
Knoppix Live GNU Linux System 9.1 on Bootable CD / DVD / USB Flash Drive
$5.99
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 16G USB Stick
$20.85
$8.00

VINTAGE SOFTWARE | KNOPPIX STD 0.1 (SECURITY TOOLS DISTRIBUTION)
$7.57
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 32G USB Stick
$21.42
$7.00
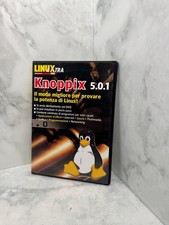
Knoppix 5.0.1 ULTRA RARE Linux DVD - Linux Pro Extra August 2006
$33.98
|
||
|
No Discussions have been posted on this vulnerability. |