|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Ubuntu Local Security Checks >> USN99-1 : php4 vulnerabilities Vulnerability Assessment Details
|
USN99-1 : php4 vulnerabilities |
||
|
php4 vulnerabilities Detailed Explanation for this Vulnerability Assessment Summary : These remote packages are missing security patches : - libapache2-mod-php4 - php4 - php4-cgi - php4-curl - php4-dev - php4-domxml - php4-gd - php4-ldap - php4-mcal - php4-mhash - php4-mysql - php4-odbc - php4-pear - php4-recode - php4-snmp - php4-sybase - php4-xslt Description : Stefano Di Paola discovered integer overflows in PHP's pack() and unpack() functions. A malicious PHP script could exploit these to break out of safe mode and execute arbitrary code with the rights of the PHP interpreter. (CVE-2004-1018) Note: The second part of CVE-2004-1018 (buffer overflow in the shmop_write() function) was already fixed in USN-66-1. Stefan Esser discovered two safe mode bypasses which permited malicious PHP scripts to circumvent path restrictions. This was possible by either using virtual_popen() with a current directory containing shell metacharacters (CVE-2004-1063) or creating a specially crafted directory whose length exceeded the capacity of the realpath() function (CVE-2004-1064). Solution : Upgrade to : - libapache2-mod-php4-4.3.8-3ubuntu7.5 (Ubuntu 4.10) - php4-4.3.8-3ubuntu7.5 (Ubuntu 4.10) - php4-cgi-4.3.8-3ubuntu7.5 (Ubuntu 4.10) - php4-curl-4.3.8-3ubuntu7.5 (Ubuntu 4.10) - php4-dev-4.3.8-3ubuntu7.5 (Ubuntu 4.10) - php4-domxml-4.3.8-3ubuntu7.5 (Ubuntu 4.10) - php4-gd-4.3.8-3ubuntu7.5 (Ubuntu 4.10) - php4-ldap-4.3.8-3ubuntu7.5 (Ubuntu 4.10) - php4-mcal-4.3.8-3ubuntu7.5 (Ubuntu 4.10) - php4-mhash-4.3.8-3ubuntu7.5 (Ubuntu 4.10) - php4-mysql-4.3.8-3ubuntu7.5 (Ubuntu 4.10) - php4-odbc-4.3.8-3 [...] Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: Ubuntu Security Notice (C) 2005 Canonical, Inc. / NASL script (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

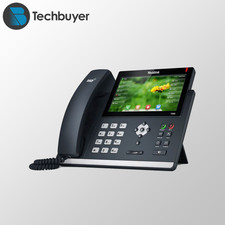
Yealink T48S VoIP/SIP Phone, 2 x Gigabit Ports PoE 7" Color SIP-T48S | TESTED
$34.95
Grandstream GXW4224 24-Line FXS Analog VoIP Gateway, Ethernet RJ-45 Black
$165.00
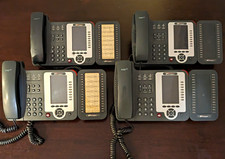
Lot of 4 USED IPitomy IP620-B with IPX-32 DSS Expansion Module VoIP Phone POE
$225.00
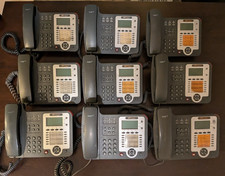
Lot of 9 Used IPitomy IP320-P HD POE Voice Speakerphone 12-Line VoIP Phone
$225.00
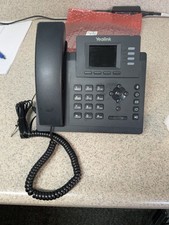
Yealink SIP-T33G IP Phone 4-LineSpeakerphone VoIP Desk Phone Black w/ Power Sply
$25.00
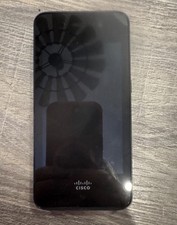
NEW Cisco CP-840 Wireless WiFi IP VoIP Phone 840 w Battery Charger Cable
$800.00
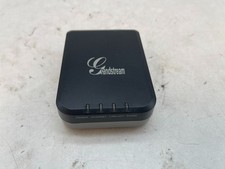
Grandstream HT701 1-Port FXS Analog Telephone Adapter ATA VoIP Gateway -Free S/H
$19.99
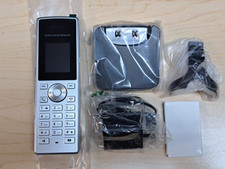
Grandstream WP810 Portable Cordless Wi-Fi IP Phone
$49.28
Set of 5 USED IPitomy IP620-B HD VoIP 6-Line IP Phone Speakerphone Ethernet POE
$149.00
SIM Bank 32 SIM Card Slots Ethernet SIM Server for GoIP
$400.00
|
||
|
No Discussions have been posted on this vulnerability. |