|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Ubuntu Local Security Checks >> USN77-1 : squid vulnerabilities Vulnerability Assessment Details
|
USN77-1 : squid vulnerabilities |
||
|
squid vulnerabilities Detailed Explanation for this Vulnerability Assessment Summary : These remote packages are missing security patches : - squid - squid-cgi - squid-common - squidclient Description : A possible authentication bypass was discovered in the LDAP authentication backend. LDAP ignores leading and trailing whitespace in search filters. This could possibly be abused to bypass explicit access controls or confuse accounting when using several variants of the login name. (CVE-2005-0173) Previous Squid versions were not strict enough while parsing HTTP requests and responses. Various violations of the HTTP protocol, such as multiple Content-Length header lines, invalid "Carriage Return" characters, and HTTP header names containing whitespace, led to cache pollution and could possibly be exploited to deliver wrong content to clients. (CVE-2005-0174) Squid was susceptible to a cache poisoning attack called "HTTP response splitting", where false replies are injected in the HTTP stream. This permited malicious web servers to forge wrong cache content for arbitrary web sites, which was then delivered to Squid clients. (CVE-2005-0175) The FSC Vulnerability Research Team discovered a buffer overflow in t [...] Solution : Upgrade to : - squid-2.5.5-6ubuntu0.4 (Ubuntu 4.10) - squid-cgi-2.5.5-6ubuntu0.4 (Ubuntu 4.10) - squid-common-2.5.5-6ubuntu0.4 (Ubuntu 4.10) - squidclient-2.5.5-6ubuntu0.4 (Ubuntu 4.10) Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: Ubuntu Security Notice (C) 2005 Canonical, Inc. / NASL script (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

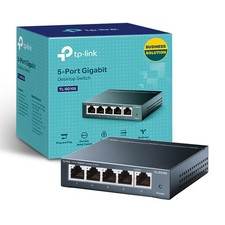
TP-Link TL-SG105 5-Port Gigabit Ethernet Unmanaged Metal Desktop Network Switch
$19.99
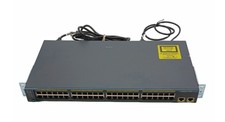
Cisco Catalyst 2960-48TT-L 48-Port Fast Ethernet Managed Rackmount Switch
$46.99
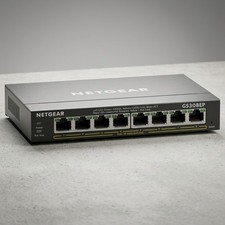
NETGEAR GS308EP Essential Series 8-Port Gigabit PoE+ Unmanaged Switch
$49.99
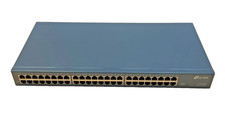
TP-Link TL-SG1048 48-Port Gigabit Rackmount Switch New Factory Sealed
$199.99
5 Port Gigabit Unmanaged Ethernet Switch, Home Network Hub, Office Ethernet S...
$9.64
10-Port Gigabit PoE Network Switch with 8 PoE+ Ports with 2 Combo SFP Slots 125W
$39.99
TP-Link TL-SG105, 5 Port Gigabit Unmanaged Ethernet Switch, Network Hub, Ethern
$15.25
Arista DCS-7010T-48-R 48P 1GbE 4P 10GbE SFP+ RA Switch with rack mounts
$69.00
NETGEAR 5-Port Gigabit Ethernet Unmanaged Switch (Gs305) - Desktop Quiet Fanless
$25.99
Linksys LGS328MPC 24-Port Managed Gigabit PoE+ Switch with 4 10G SFP+ Uplinks
$224.95
|
||
|
No Discussions have been posted on this vulnerability. |