|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Ubuntu Local Security Checks >> USN288-1 : postgresql-7.4/-8.0, postgresql, psycopg, Vulnerability Assessment Details
|
USN288-1 : postgresql-7.4/-8.0, postgresql, psycopg, |
||
|
postgresql-7.4/-8.0, postgresql, psycopg, Detailed Explanation for this Vulnerability Assessment Summary : These remote packages are missing security patches : - libecpg-compat2 - libecpg-dev - libecpg4 - libecpg5 - libpgtcl - libpgtcl-dev - libpgtypes2 - libpq-dev - libpq3 - libpq4 - postgresql - postgresql-7.4 - postgresql-8.0 - postgresql-client - postgresql-client-7.4 - postgresql-client-8.0 - postgresql-contrib - postgresql-contrib-7.4 - postgresql-contrib-8.0 - postgresql-dev - postgresql-doc - postgresql-doc-7.4 - postgresql-doc-8.0 - postgresql-plperl-7.4 - postgresql-plperl-8.0 [...] Description : CVE-2006-2313: Akio Ishida and Yasuo Ohgaki discovered a weakness in the handling of invalidly-encoded multibyte text data. If a client application processed untrusted input without respecting its encoding and applied standard string escaping techniques (such as replacing a single quote >>'<< with >>\'<< or >>''<<), the PostgreSQL server could interpret the resulting string in a way that permited a possible hacker to inject arbitrary SQL commands into the resulting SQL query. The PostgreSQL server has been modified to reject such invalidly encoded strings now, which completely fixes the problem for some 'safe' multibyte encodings like UTF-8. CVE-2006-2314: However, there are some less popular and client-only multibyte encodings (such as SJIS, BIG5, GBK, GB18030, and UHC) which contain valid multibyte characters that end with the byte 0x5c, which is the representation of the backslash character >>\<< in ASCII. Many client libraries and applications use the non-standard, but pop [...] Solution : Upgrade to : - libecpg-compat2-8.0.3-15ubuntu2.2 (Ubuntu 5.10) - libecpg-dev-8.0.3-15ubuntu2.2 (Ubuntu 5.10) - libecpg4-7.4.7-2ubuntu2.3 (Ubuntu 5.04) - libecpg5-8.0.3-15ubuntu2.2 (Ubuntu 5.10) - libpgtcl-7.4.7-2ubuntu2.3 (Ubuntu 5.04) - libpgtcl-dev-7.4.7-2ubuntu2.3 (Ubuntu 5.04) - libpgtypes2-8.0.3-15ubuntu2.2 (Ubuntu 5.10) - libpq-dev-8.0.3-15ubuntu2.2 (Ubuntu 5.10) - libpq3-7.4.8-17ubuntu1.3 (Ubuntu 5.10) - libpq4-8.0.3-15ubuntu2.2 (Ubuntu 5.10) - postgresql-7.4.7-2ubuntu2.3 (Ubuntu 5.04) - postgresql [...] Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: Ubuntu Security Notice (C) 2005 Canonical, Inc. / NASL script (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

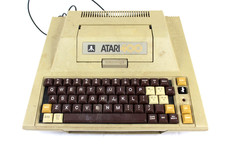
VTG Atari 400 Home Computer System ** Sold "AS-IS" for Parts or Repair
$88.75
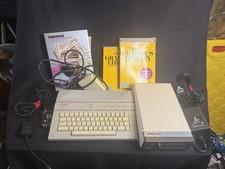
Atari 130 XE/Atari 1050 Bundle W/ Cords And Extras (Powered On)
$300.00
DEFECTIVE Atari 810 Vintage Computer Disk Drive powers on Unit Only Boo G3D
$49.29
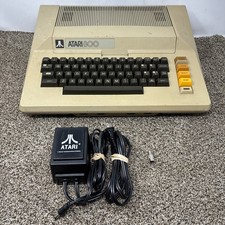
Atari 800 8-bit Computer System Fully Tested Great Condition 48k READ
$350.00
Atari XE 130XE Computer NTSC with Power Supply Powers On Untested
$159.95
Fujinet 1.7.1 Atari 400 800 800XL 130XE 65XE XEGS Assembled, Tested, Working
$99.99
ATARI Mouse with Adapter for ST, STE, Mega STE, TT Optical - USA Seller
$29.99
INFO/soft Character Generator Manual for Atari 3000/5000/7000 NTSC
$40.00
UNOCART-2600 SD card Multi Rom Cartridge for ATARI 2600 with CASE
$34.25
Vintage Atari SF354 Floppy Disk Drive & Power Supply FOR PARTS OR REPAIR AS IS
$120.00
|
||
|
No Discussions have been posted on this vulnerability. |