|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Ubuntu Local Security Checks >> USN260-1 : flex vulnerability Vulnerability Assessment Details
|
USN260-1 : flex vulnerability |
||
|
flex vulnerability Detailed Explanation for this Vulnerability Assessment Summary : These remote packages are missing security patches : - cpp-3.3 - cpp-3.3-doc - cpp-3.4 - cpp-3.4-doc - fastjar - fixincludes - flex - flex-doc - g++-3.3 - g++-3.4 - g77-3.3 - g77-3.3-doc - g77-3.4 - g77-3.4-doc - gcc-3.3 - gcc-3.3-base - gcc-3.3-doc - gcc-3.4 - gcc-3.4-base - gcc-3.4-doc - gcj-3.3 - gcj-3.4 - gij-3.3 - gij-3.4 - gnat-3.3 - gnat-3.3-doc - gnat-3.4 - gnat-3.4-doc - gobjc-3.3 - gobjc-3.4 - gpc-2.1-3.3 - gpc-2.1-3.3-doc - gpc-2.1-3.4 - gpc-2.1-3.4-doc - lib32g [...] Description : Chris Moore discovered a buffer overflow in a particular class of lexicographical scanners generated by flex. This could be exploited to execute arbitrary code by processing specially crafted user-defined input to an application that uses a flex scanner for parsing. This flaw particularly affects gpc, the GNU Pascal Compiler. A potentially remote attacker could exploit this by tricking an user or automated system into compiling a specially crafted Pascal source code file. Please note that gpc is not officially supported in Ubuntu (it is in the 'universe' component of the archive). However, this affects you if you use a customized version built from the gcc-3.3 or gcc-3.4 source package (which is supported). Solution : Upgrade to : - cpp-3.3-3.3.5-8ubuntu2.1 (Ubuntu 5.04) - cpp-3.3-doc-3.3.5-8ubuntu2.1 (Ubuntu 5.04) - cpp-3.4-3.4.4-6ubuntu8.1 (Ubuntu 5.10) - cpp-3.4-doc-3.4.4-6ubuntu8.1 (Ubuntu 5.10) - fastjar-3.4.2-2ubuntu1.1 (Ubuntu 4.10) - fixincludes-3.3.4-9ubuntu5.1 (Ubuntu 4.10) - flex-2.5.31-31ubuntu0.5.10.1 (Ubuntu 5.10) - flex-doc-2.5.31-31ubuntu0.5.10.1 (Ubuntu 5.10) - g++-3.3-3.3.5-8ubuntu2.1 (Ubuntu 5.04) - g++-3.4-3.4.4-6ubuntu8.1 (Ubuntu 5.10) - g77-3.3-3.3.5-8ubuntu2.1 (Ubuntu 5.04) - g77-3.3-doc-3.3.5-8u [...] Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: Ubuntu Security Notice (C) 2005 Canonical, Inc. / NASL script (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

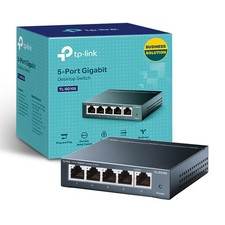
TP-Link TL-SG105 5-Port Gigabit Ethernet Unmanaged Metal Desktop Network Switch
$19.99
Cisco Catalyst 2960-48TT-L 48-Port Fast Ethernet Managed Rackmount Switch
$46.99
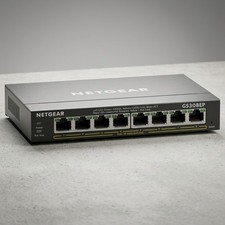
NETGEAR GS308EP Essential Series 8-Port Gigabit PoE+ Unmanaged Switch
$49.99
TP-Link TL-SG1048 48-Port Gigabit Rackmount Switch New Factory Sealed
$199.99
5 Port Gigabit Unmanaged Ethernet Switch, Home Network Hub, Office Ethernet S...
$9.64
10-Port Gigabit PoE Network Switch with 8 PoE+ Ports with 2 Combo SFP Slots 125W
$39.99
Arista DCS-7010T-48-R 48P 1GbE 4P 10GbE SFP+ RA Switch with rack mounts
$69.00
TP-Link TL-SG2210P 10-Port Gigabit Smart Switch w/ 8-Port PoE+ NO AC SKU 25597
$36.98
NETGEAR 5-Port Gigabit Ethernet Unmanaged Switch (Gs305) - Desktop Quiet Fanless
$25.99
Linksys LGS328MPC 24-Port Managed Gigabit PoE+ Switch with 4 10G SFP+ Uplinks
$224.95
|
||
|
No Discussions have been posted on this vulnerability. |