|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Ubuntu Local Security Checks >> USN199-1 : linux-source-2.6.10, linux-source-2.6.8.1 vulnerabilities Vulnerability Assessment Details
|
USN199-1 : linux-source-2.6.10, linux-source-2.6.8.1 vulnerabilities |
||
|
linux-source-2.6.10, linux-source-2.6.8.1 vulnerabilities Detailed Explanation for this Vulnerability Assessment Summary : These remote packages are missing security patches : - linux-doc-2.6.10 - linux-doc-2.6.8.1 - linux-headers-2.6.10-5 - linux-headers-2.6.10-5-386 - linux-headers-2.6.10-5-686 - linux-headers-2.6.10-5-686-smp - linux-headers-2.6.10-5-amd64-generic - linux-headers-2.6.10-5-amd64-k8 - linux-headers-2.6.10-5-amd64-k8-smp - linux-headers-2.6.10-5-amd64-xeon - linux-headers-2.6.10-5-k7 - linux-headers-2.6.10-5-k7-smp - linux-headers-2.6.10-5-power3 - linux-headers-2.6.10-5-power3-smp - linux-header [...] Description : A Denial of Service vulnerability was discovered in the sys_set_mempolicy() function. By calling the function with a negative first argument, a local attacker could cause a kernel crash. (CVE-2005-3053) A race condition was discovered in the handling of shared memory mappings with CLONE_VM. A local attacker could exploit this to cause a deadlock (Denial of Service) by triggering a core dump while waiting for a thread which had just performed an exec() system call. (CVE-2005-3106) A race condition was found in the handling of traced processes. When one thread was tracing another thread that shared the same memory map, a local attacker could trigger a deadlock (Denial of Service) by forcing a core dump when the traced thread was in the TASK_TRACED state. (CVE-2005-3107) A vulnerability has been found in the "ioremap" module. By performing certain IO mapping operations, a local attacker could either read memory pages he has not normally access to (information leak) or cause a kernel crash (Denial of Servic [...] Solution : Upgrade to : - linux-doc-2.6.10-2.6.10-34.7 (Ubuntu 5.04) - linux-doc-2.6.8.1-2.6.8.1-16.24 (Ubuntu 4.10) - linux-headers-2.6.10-5-2.6.10-34.7 (Ubuntu 5.04) - linux-headers-2.6.10-5-386-2.6.10-34.7 (Ubuntu 5.04) - linux-headers-2.6.10-5-686-2.6.10-34.7 (Ubuntu 5.04) - linux-headers-2.6.10-5-686-smp-2.6.10-34.7 (Ubuntu 5.04) - linux-headers-2.6.10-5-amd64-generic-2.6.10-34.7 (Ubuntu 5.04) - linux-headers-2.6.10-5-amd64-k8-2.6.10-34.7 (Ubuntu 5.04) - linux-headers-2.6.10-5-amd64-k8-smp-2.6.10-34.7 (Ubuntu 5 [...] Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: Ubuntu Security Notice (C) 2005 Canonical, Inc. / NASL script (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

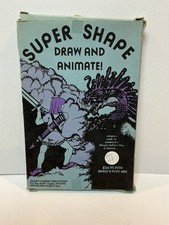
Vintage Apple II Avant-Garde Creations Super Shape Draw And Animate 1981
$295.00
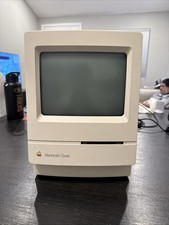
Apple Macintosh Classic M1420 Vintage Desktop Computer Model Macintosh Classic
$100.00
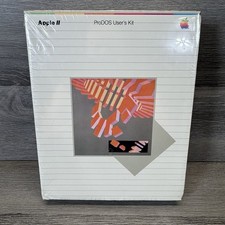
Vintage 1983 Apple II ProDOS User's Kit Computer Software NEW SEALED A2D2010
$64.95
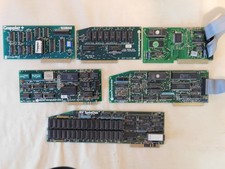
Apple Computer cards VTG 670-8020-B 607-0103-C 607-0291-C AST -Orange Micro ++
$169.00
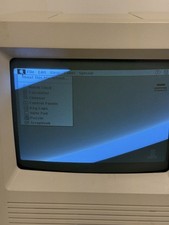
READ - Vintage Apple Macintosh SE/30 - Boots
$850.00
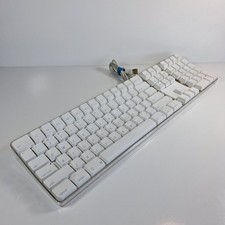
Vintage Apple Mac A1048 White Wired Full Size Keyboard w/ 2 USB Ports TESTED
$29.00
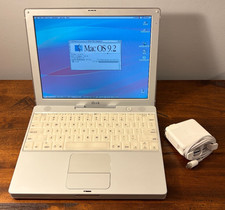
Vintage Apple iBook G3 12.1” 500MHz 2001 Restored, SSD Upgraded Mac OS 9.2/OS X
$180.00
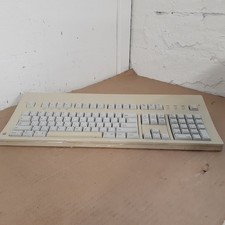
Vintage Apple Extended Keyboard- M0115 - no cord
$49.99
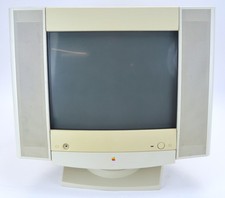
Vintage Apple Multiple Scan 15av Display Monitor M4681
$299.99
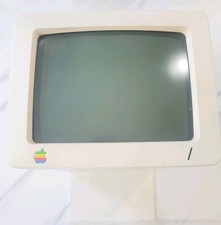
Vintage Apple Monitor IIc 9" Green Monochrome 06/1985 A2M4090 October 1984 Stand
$275.00
|
||
|
No Discussions have been posted on this vulnerability. |