|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Ubuntu Local Security Checks >> USN178-1 : linux-source-2.6.10, linux-source-2.6.8.1 vulnerabilities Vulnerability Assessment Details
|
USN178-1 : linux-source-2.6.10, linux-source-2.6.8.1 vulnerabilities |
||
|
linux-source-2.6.10, linux-source-2.6.8.1 vulnerabilities Detailed Explanation for this Vulnerability Assessment Summary : These remote packages are missing security patches : - linux-doc-2.6.10 - linux-doc-2.6.8.1 - linux-headers-2.6.10-5 - linux-headers-2.6.10-5-386 - linux-headers-2.6.10-5-686 - linux-headers-2.6.10-5-686-smp - linux-headers-2.6.10-5-amd64-generic - linux-headers-2.6.10-5-amd64-k8 - linux-headers-2.6.10-5-amd64-k8-smp - linux-headers-2.6.10-5-amd64-xeon - linux-headers-2.6.10-5-itanium - linux-headers-2.6.10-5-itanium-smp - linux-headers-2.6.10-5-k7 - linux-headers-2.6.10-5-k7-smp - linux-head [...] Description : Oleg Nesterov discovered a local Denial of Service vulnerability in the timer handling. When a non group-leader thread called exec() to execute a different program while an itimer was pending, the timer expiry would signal the old group leader task, which did not exist any more. This caused a kernel panic. This vulnerability only affects Ubuntu 5.04. (CVE-2005-1913) Al Viro discovered that the sendmsg() function did not sufficiently validate its input data. By calling sendmsg() and at the same time modifying the passed message in another thread, he could exploit this to execute arbitrary commands with kernel rights. This only affects the amd64 bit platform. (CVE-2005-2490) Al Viro discovered a vulnerability in the raw_sendmsg() function. By calling this function with specially crafted arguments, a local attacker could either read kernel memory contents (leading to information disclosure) or manipulate the hardware state by reading certain IO ports. This vulnerability only affects Ubuntu 5.04. (CAN-200 [...] Solution : Upgrade to : - linux-doc-2.6.10-2.6.10-34.5 (Ubuntu 5.04) - linux-doc-2.6.8.1-2.6.8.1-16.22 (Ubuntu 4.10) - linux-headers-2.6.10-5-2.6.10-34.5 (Ubuntu 5.04) - linux-headers-2.6.10-5-386-2.6.10-34.5 (Ubuntu 5.04) - linux-headers-2.6.10-5-686-2.6.10-34.5 (Ubuntu 5.04) - linux-headers-2.6.10-5-686-smp-2.6.10-34.5 (Ubuntu 5.04) - linux-headers-2.6.10-5-amd64-generic-2.6.10-34.5 (Ubuntu 5.04) - linux-headers-2.6.10-5-amd64-k8-2.6.10-34.5 (Ubuntu 5.04) - linux-headers-2.6.10-5-amd64-k8-smp-2.6.10-34.5 (Ubuntu 5 [...] Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: Ubuntu Security Notice (C) 2005 Canonical, Inc. / NASL script (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

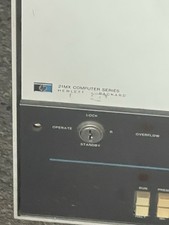
Vintage HP 21MX 1000 M-Series Minicomputer Chassis Backplane Parts AS-IS
$325.99
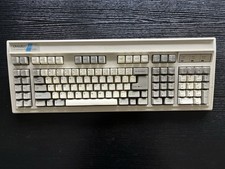
Vintage Computer Keyboard Northgate OMNIKEY Ultra
$120.00
Sealed Vintage Intel Pro/1000 Network Adapters Drivers CD Ver 3.1 Vintage PC NEW
$39.61
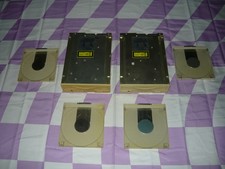
Lot of 2 Vintage Plextor PX-43CS SCSI CD-ROM Caddy Drives + 4 Caddies Used
$55.99
Original Vintage Old Style STANDARD Black CD Jewel Case (Heavy Duty) 90g Lot
$316.95
Dell Latitude XPi CD P150ST Vintage Computer - Not Working
$70.00
Vintage NEC Versa V/50 Notebook Computer with UNTESTED as/is
$29.99
RAM-Tester for vintage RAM, 4816, 4164, 41256, 514402, and more - USA Seller
$35.00
Vintage Hewlett Packard HP 13181-60074 Circuit Card Assembly / Interface Board.
$135.37
VINTAGE COLLECTIBLE Comp USA Maxtor 20 GB 3.5 Inch EIDE Hard Drive NEW SEALED
$500.00
|
||
|
No Discussions have been posted on this vulnerability. |