|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Ubuntu Local Security Checks >> USN157-1 : mozilla-thunderbird vulnerabilities Vulnerability Assessment Details
|
USN157-1 : mozilla-thunderbird vulnerabilities |
||
|
mozilla-thunderbird vulnerabilities Detailed Explanation for this Vulnerability Assessment Summary : These remote packages are missing security patches : - mozilla-enigmail - mozilla-thunderbird - mozilla-thunderbird-dev - mozilla-thunderbird-enigmail - mozilla-thunderbird-inspector - mozilla-thunderbird-offline - mozilla-thunderbird-typeaheadfind Description : Vladimir V. Perepelitsa discovered a bug in Thunderbird's handling of anonymous functions during regular expression string replacement. A malicious HTML email could exploit this to capture a random block of client memory. (CVE-2005-0989) Georgi Guninski discovered that the types of certain XPInstall related JavaScript objects were not sufficiently validated when they were called. This could be exploited by malicious HTML email content to crash Thunderbird or even execute arbitrary code with the rights of the user. (CVE-2005-1159) Thunderbird did not properly verify the values of XML DOM nodes. By tricking the user to perform a common action like clicking on a link or opening the context menu, a malicious HTML email could exploit this to execute arbitrary JavaScript code with the full rights of the user. (CVE-2005-1160) A variant of the attack described in CVE-2005-1160 (see USN-124-1) was discovered. Additional checks were added to make sure Javascript eval and script objects are run with the p [...] Solution : Upgrade to : - mozilla-enigmail-0.92-1ubuntu05.04.1 (Ubuntu 5.04) - mozilla-thunderbird-1.0.6-0ubuntu05.04 (Ubuntu 5.04) - mozilla-thunderbird-dev-1.0.6-0ubuntu05.04 (Ubuntu 5.04) - mozilla-thunderbird-enigmail-0.92-1ubuntu05.04.1 (Ubuntu 5.04) - mozilla-thunderbird-inspector-1.0.6-0ubuntu05.04 (Ubuntu 5.04) - mozilla-thunderbird-offline-1.0.6-0ubuntu05.04 (Ubuntu 5.04) - mozilla-thunderbird-typeaheadfind-1.0.6-0ubuntu05.04 (Ubuntu 5.04) Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: Ubuntu Security Notice (C) 2005 Canonical, Inc. / NASL script (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

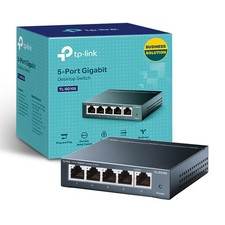
TP-Link TL-SG105 5-Port Gigabit Ethernet Unmanaged Metal Desktop Network Switch
$19.99
Cisco Catalyst 2960-48TT-L 48-Port Fast Ethernet Managed Rackmount Switch
$46.99
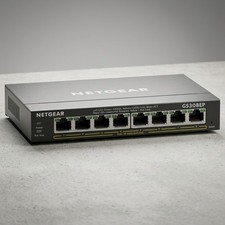
NETGEAR GS308EP Essential Series 8-Port Gigabit PoE+ Unmanaged Switch
$49.99
TP-Link TL-SG1048 48-Port Gigabit Rackmount Switch New Factory Sealed
$199.99
5 Port Gigabit Unmanaged Ethernet Switch, Home Network Hub, Office Ethernet S...
$9.64
10-Port Gigabit PoE Network Switch with 8 PoE+ Ports with 2 Combo SFP Slots 125W
$39.99
Arista DCS-7010T-48-R 48P 1GbE 4P 10GbE SFP+ RA Switch with rack mounts
$69.00
TP-Link TL-SG2210P 10-Port Gigabit Smart Switch w/ 8-Port PoE+ NO AC SKU 25597
$36.98
NETGEAR 5-Port Gigabit Ethernet Unmanaged Switch (Gs305) - Desktop Quiet Fanless
$25.99
Linksys LGS328MPC 24-Port Managed Gigabit PoE+ Switch with 4 10G SFP+ Uplinks
$224.95
|
||
|
No Discussions have been posted on this vulnerability. |