|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Ubuntu Local Security Checks >> USN118-1 : postgresql vulnerabilities Vulnerability Assessment Details
|
USN118-1 : postgresql vulnerabilities |
||
|
postgresql vulnerabilities Detailed Explanation for this Vulnerability Assessment Summary : These remote packages are missing security patches : - libecpg-dev - libecpg4 - libpgtcl - libpgtcl-dev - libpq3 - postgresql - postgresql-client - postgresql-contrib - postgresql-dev - postgresql-doc Description : It was discovered that unprivileged users were permited to call internal character conversion functions. However, since these functions were not designed to be safe against malicious choices of argument values, this could potentially be exploited to execute arbitrary code with the rights of the PostgreSQL server (user "postgres"). (CVE-2005-1409) Another vulnerability was found in the "tsearch2" module of postgresql-contrib. This module declared several functions as internal, although they did not accept any internal argument this breaks the type safety of "internal" by permiting users to construct SQL commands that invoke other functions accepting "internal" arguments. This could eventually be exploited to crash the server, or possibly even execute arbitrary code with the rights of the PostgreSQL server. (CVE-2005-1410) These vulnerabilities must also be fixed in all existing databases when upgrading. The post-installation script of the updated package attempts to do this automatically if the pack [...] Solution : Upgrade to : - libecpg-dev-7.4.7-2ubuntu2.1 (Ubuntu 5.04) - libecpg4-7.4.7-2ubuntu2.1 (Ubuntu 5.04) - libpgtcl-7.4.7-2ubuntu2.1 (Ubuntu 5.04) - libpgtcl-dev-7.4.7-2ubuntu2.1 (Ubuntu 5.04) - libpq3-7.4.7-2ubuntu2.1 (Ubuntu 5.04) - postgresql-7.4.7-2ubuntu2.1 (Ubuntu 5.04) - postgresql-client-7.4.7-2ubuntu2.1 (Ubuntu 5.04) - postgresql-contrib-7.4.7-2ubuntu2.1 (Ubuntu 5.04) - postgresql-dev-7.4.7-2ubuntu2.1 (Ubuntu 5.04) - postgresql-doc-7.4.7-2ubuntu2.1 (Ubuntu 5.04) Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: Ubuntu Security Notice (C) 2005 Canonical, Inc. / NASL script (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

SFP TO RJ45 TRANSCEIVER SFP MODULE COPPER SFP OPTICAL PORT TO RJ45 ETHERNET PORT
$7.99
Dell Intel X710-DA2 5N7Y5 Dual-Port 10GbE SFP+ PCIe 3.0 x8 Network Adapter
$27.50
Cisco Acacia DP04QSDD-E25-840 400G QSFP-DD Coherent DCO Transceiver Module
$699.99

Cisco QSFP-40G-SR-BD Module 10-2945-02 NEW CLAMSHELL
$45.50
SolarFlare XtremeScale X2522-25G-PLUS Dual Port 25G SFP28 PCI-E 3.1 x8 NIC FH LP
$899.99

Genuine Cisco SFP-10G-SR 0-2415-03 10 Gigabit Transceiver
$5.40
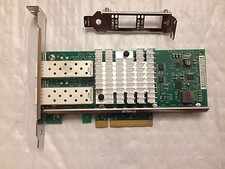
Intel X520-DA2 10Gb 10Gbe 10 Gigabit Network Adapter NIC Dual Port E10G42BTDA
$28.94
HP 560SFP+ 10GB 2-port PCIe NIC Ethernet ADAPTER 669279-001 w/ (2) 10GB SFP+
$16.99
NEW Sealed Cisco SFP-10G-LR 10GBASE-LR SFP+ 1310nm 10km *US Shipping*
$24.00
Dell 10 Gigabit SFP+ SR Transceiver 0XYD50 NEW SEALED
$24.99
|
||
|
No Discussions have been posted on this vulnerability. |