|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SuSE Local Security Checks >> SuSE-SA:2003:048: gpg Vulnerability Assessment Details
|
SuSE-SA:2003:048: gpg |
||
|
Check for the version of the gpg package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory SuSE-SA:2003:048 (gpg). The gnupg (the SUSE package is named gpg) package is the most widely used software for cryptographic encryption/decryption of data. Two independent errors have been found in gpg (GnuPG) packages as shipped with SUSE products: A) A format string error in the client code that does key retrieval from a (public) key server B) A cryptographic error in gpg that results in a compromise of a cryptographic keypair if ElGamal signing keys have been used for generating the key. A) There exists a format string error in thhe client code for key retrieval from a keyserver. gpg-1.2.x version packages are affected by this vulnerability. The format string error can be used by a possible hacker performing a man-in-the-middle-attack between you and your keyserver, or by a compromised keyserver. The result is a crash of gpg or a potential execution of arbitrary code provided by the attacker, if the keyserver is used for key retrieval at the time of the attack. B) Werner Koch, the author of the gpg package, has publicly announced a weakness in gpg that has been reported to him by Phong Nguyen: ElGamal signing keys can be attacked within seconds to reveal the private key of the keypair. It is strongly advised that ElGamal signing keys should be revoked immediately. Only ElGamal keys are affected, other types are not vulnerable. To find out if you are using an ElGamal signing key, list your public keys using the command gpg --list-keys your_keyid Example: $ gpg --list-keys [email protected] pub 1024D/9C800ACA 2000-10-19 SuSE Package Signing Key sub 2048g/8495160C 2000-10-19 [expires: 2006-02-12] $ If your key lists a capital 'G' after the key's length (like in pub 1536G/...), then your key is vulnerable. A small letter 'g' after the key length does NOT indicate any problem. ElGamal keys can be used for primary keys as well as for subkeys. In the case where only a subkey is an ElGamal key, it is sufficient to revoke this specific subkey. To revoke a key, generate a revocation certificate using the following command: gpg --gen-revoke your_keyid > revocation_certificate.pgp Then, the revokation certificate must be imported into your keyring: gpg --import < revocation_certificate.pgp As your last action, send the key with its revocation certificate to the keyservers that know your key: gpg --keyserver wwwkeys.eu.pgp.net --send-keys your_keyid ElGamal keys can only be generated by gpg if a special option (--expert) has been used to reveal 'expert' options, and if a warning has been ignored after your choice to use ElGamal keys. Such keys are rare (Werner Koch reports 848 primary ElGamal signing keys and 324 vulnerable subkeys on the keyservers.). Therefore, we expect that only experienced users of gpg may be vulnerable to the ElGamal signing key error. Solution : http://www.suse.de/security/2003_048_gpg.html Network Security Threat Level: Medium Networks Security ID: 9115 Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

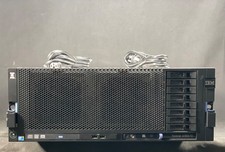
IBM System X3850-X5 Server w/4x Intel Xeon E7-4870 CPU , 512 GB DDR3 RAM,NO HDD
$1299.99
IBM ADP Server Type 7870 AC1 NO HDD | 128GB RAM PC3L | 2 x Xeon E5620
$199.99
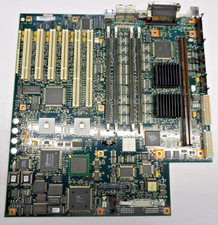
Unused IBM 09P0037 MAINBOARD For RS/6000 7044-170 P-Series
$375.00
IBM QRadar xx29 2x Xeon E5-2650v4 2x 900W PSU M5120 12x 3.5" Bay Server No RAM
$179.99
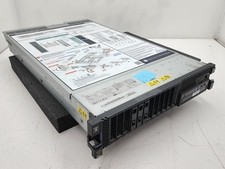
IBM Power 8 S822L Server 8247-22L POWER8 Enterprise 256GB RAM 2x 00KV626 CPU
$999.99
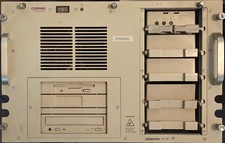
Compaq ProLiant 1500R 5/100 rack server, Series 3155, with IBM 2.1GB HD, VINTAGE
$295.00
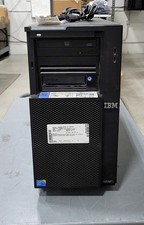
IBM SYSTEM X3500 M3 SERVER 7380AC1 TOWER Server XEON E5620 8GB RAID SEE NOTES
$110.30
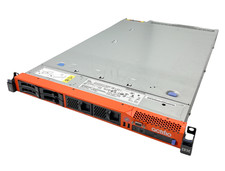
IBM System x3550 M3 1U Server 2x Xeon E5645, 192GB RAM, 2x 300GB HDD (7944-AC1)
$150.00
Rare Vintage IBM 93ZZ PowerPC Server Board - MCM Ceramic CPU - 40N1844 - 1.1 lbs
$49.99
Lot of 3 IBM 00JY196 ServeRAID M1210 PCI Express SAS SATA Storage Controller
$68.99
|
||
|
No Discussions have been posted on this vulnerability. |