|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SuSE Local Security Checks >> SuSE-SA:2003:047: bind8 Vulnerability Assessment Details
|
SuSE-SA:2003:047: bind8 |
||
|
Check for the version of the bind8 package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory SuSE-SA:2003:047 (bind8). To resolve IP addresses to host and domain names and vice versa the DNS service needs to be consulted. The most popular DNS software is the BIND8 and BIND9 suite. The BIND8 code is vulnerable to a remote denial-of-service attack by poisoning the cache with authoritative negative responses that should not be accepted otherwise. To execute this attack a name-server needs to be under malicious control and the victim's bind8 has to query this name-server. The attacker can set a high TTL value to keep his negative record as long as possible in the cache of the victim. For this time the clients of the attacked site that rely on the bind8 service will not be able to reach the domain specified in the negative record. These records should disappear after the time-interval (TTL) elapsed. There is no temporary workaround for this bug. To make this update effective run 'rcnamed restart' as root please. Please download the update package for your distribution and verify its integrity by the methods listed in section 3) of this announcement. Then, install the package using the command 'rpm -Fhv file.rpm' to apply the update. Solution : http://www.suse.de/security/2003_47_bind8.html Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

AMD Ryzen 5 5500 Processor ( read Description)
$59.00
(LOT OF 20) Intel Core i5-8400 CPU 2.80GHz Desktop Processor (SR3QT)
$700.00
INTEL CORE I9-10940X X-SERIES PROCESSOR | 3.30GHZ | SRGSH
$179.99
Compo MSI B150I GAMING PRO AC LGA1151 16 Gb DDR4 + Cpu I7 6700+I/O Shields.
$159.00
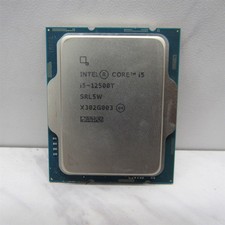
Intel Core i5-12500T SRL5W 2GHz 18MB 6 Core Socket LGA1700 Desktop CPU Processor
$114.99
Intel Core i7-9700 Octa-Core 3 GHz Desktop Processor LGA 1151
$79.99
Intel Core i7-3770K 3.5 GHz Processor
$39.00
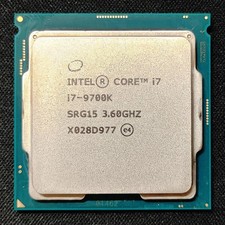
Intel Core i7-9700K Octa-Core 3.6 GHz Desktop CPU
$99.99
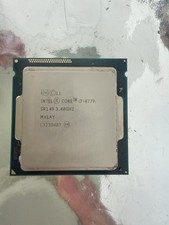
Intel Core i7-4770 3.40GHz Quad Core SR149 LGA 1150 CPU Processor tested
$35.00
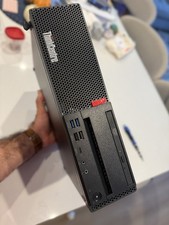
Lenovo ThinkCentre M920s SFF Barebones PC Motherboard PSU DVD No CPU RAM SSD
$27.99
|
||
|
No Discussions have been posted on this vulnerability. |