|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SuSE Local Security Checks >> SUSE-SA:2006:057: kernel Vulnerability Assessment Details
|
SUSE-SA:2006:057: kernel |
||
|
Check for the version of the kernel package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory SUSE-SA:2006:057 (kernel). Various security problems were found and fixed in the Linux kernel. We have released updates for following distributions: - SUSE Linux Enterprise Server 9 (on September 21st) - SUSE Linux Enterprise 10 (on September 26th) - SUSE Linux 9.2 up to 10.1 (on September 14th) The SUSE Linux Enterprise Server 10 kernel for the S/390 platform is still pending due to platform specific issues found in QA and waiting for further analysis. Following security issues have been addressed: - CVE-2006-3745: A double user space copy in a SCTP ioctl permits local attackers to overflow a buffer in the kernel, potentially permiting code execution and privilege escalation. - CVE-2006-4093: Local attackers were able to crash PowerPC systems with PPC970 processor using a not correctly disabled privileged instruction ('attn'). - CVE-2006-3468: Remote attackers able to access an NFS of a ext2 or ext3 filesystem can cause a denial of service (file system panic) via a crafted UDP packet with a V2 look up procedure that specifies a bad file handle (inode number), which triggers an error and causes an exported directory to be remounted read-only. - Matthias Andree reported a deadlock in the NFS lockd to us, where a remote attacker with access to lockd was able to at least crash the lockd kernel process and so render NFS exports from this server unusable. This problem existed only in the SUSE Linux 9.2 up to 10.0 kernels. The SUSE Linux Enterprise kernels also received a number of bugfixes, not listed here (please refer to the Novell TID pages listed below). Solution : http://www.suse.de/security/http://www.novell.com/linux/security/advisories/2006_57_kernel.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2007 Tenable Network Security |
||
|
Cables, Connectors |

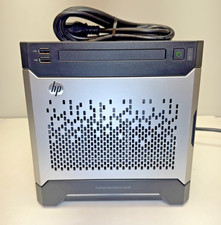
HP ProLiant MicroServer Gen8 G1610T @2.3 GHz, 16GB, 712317-001 NO HDD/OS
$199.00
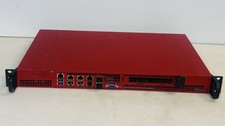
Supermicro 1U Network Server Appliance 16GB RAM 800GB SSD 6 LAN Ports Powers On
$450.00
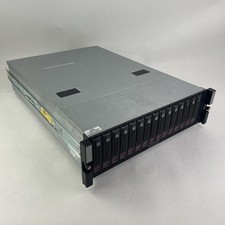
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
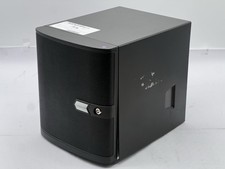
Nasuni NF-50 Supermicro Server, Atom CPU C2558, @ 2.40GHz, 8GB RAM-No HDD/OS/AC
$250.00
New Barebones Supermicro 5019D Server, 4C/8T Xeon D-2123T, 1U Rackmountable, 10G
$449.99
Supermicro 2U X10DRU-i 2x E5-2680 v3 2.5ghz 32gb Ram 240gb SSD 2x GPU *READ*
$369.99
Supermicro CSE-815-5 4B LFF Xeon E3-1245v6 16GB DDR4 1x 9361-8i 4x 1TB SATA HDD
$483.99
Supermicro 5019D-4C-FN8TP Xeon D-2123IT (4C/8T) 64GB DDR4 10GbE 480GB 1U Server
$689.00
$280.00
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
|
||
|
No Discussions have been posted on this vulnerability. |