|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SuSE Local Security Checks >> SUSE-SA:2006:040: OpenOffice_org Vulnerability Assessment Details
|
SUSE-SA:2006:040: OpenOffice_org |
||
|
Check for the version of the OpenOffice_org package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory SUSE-SA:2006:040 (OpenOffice_org). Following security problems were found and fixed in OpenOffice_org: - CVE-2006-2198: A security vulnerability in OpenOffice.org may make it possible to inject basic code into documents which is executed upon loading of the document. The user will not be asked or notified and the macro will have full access to system resources with current user's rights. As a result, the macro may delete/replace system files, read/send private data and/or cause additional security issues. Note that this attack works even with Macro execution disabled. This attack permits remote attackers to modify files / execute code as the user opening the document. - CVE-2006-2199: A security vulnerability related to OpenOffice.org documents may permit certain Java applets to break through the 'sandbox' and therefore have full access to system resources with current user rights. The offending Applets may be constructed to destroy/replace system files, read or send private data, and/or cause additional security issues. Since Java applet support is only there for historical reasons, as StarOffice was providing browser support, the support has now been disabled by default. - CVE-2006-3117: A buffer overflow in the XML UTF8 converter permits for a value to be written to an arbitrary location in memory. This may lead to command execution in the context of the current user. Solution : http://www.suse.de/security/http://www.novell.com/linux/security/advisories/2006_40_openoffice.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2007 Tenable Network Security |
||
|
Cables, Connectors |

Dell 6P85J 4TB ST4000NM0063 7.2k 6Gb/s 3.5” SAS SED Hard Drive with Tray
$39.99
Western Digital HUS726T4TAL5204 4TB 7.2K SAS 12Gb/s 3.5" 512e HDD NetApp X375A
$64.00
Western Digital 0B36404 Ultrastar DC HC320 8TB 7200RPM SATA HDD, HUS728T8TALE6L4
$250.00

Western Digital 1TB 3.5" SATA III 7200RPM Desktop Hard Drive
$34.99
Seagate Exos ST20000NM003C 20TB CMR 7200RPM SATA6Gb/s 3.5" Enterprise Hard Drive
$509.99
Western Digital WD Blue WD10EZEX 1 TB 3.5" SATA III Desktop Hard Drive
$23.99
Dell ST6000NM0034 1HT27Z-150 NWCCG 6TB SAS 3.5 7.2K ENTERPRISE SERVER DRIVE
$68.99
Seagate Exos ST2000NX0253 HDD 2TB SATA 7.2K 2.5" 512b/s
$55.00
DELL 2TB Enterprise HDD (7200RPM, 3.5", SATA III, 128MB Cache) HUS722T2TALA600
$49.95
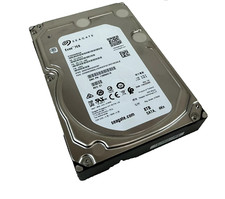
(ST8000NM0045) SEAGATE ENTERPRISE 8TB 7200RPM 4Kn SATA 6Gb/s 3.5" HARD DRIVE
$199.99
|
||
|
No Discussions have been posted on this vulnerability. |