|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SuSE Local Security Checks >> SUSE-SA:2006:030: postgresql Vulnerability Assessment Details
|
SUSE-SA:2006:030: postgresql |
||
|
Check for the version of the postgresql package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory SUSE-SA:2006:030 (postgresql). Two character set encoding related security problems were fixed in the PostgreSQL database server: CVE-2006-2313: Akio Ishida and Yasuo Ohgaki discovered a weakness in the handling of invalidly-encoded multibyte text data. If a client application processed untrusted input without respecting its encoding and applied standard string escaping techniques (such as replacing a single quote >>'<< with >>\'<< or >>''<<), the PostgreSQL server could interpret the resulting string in a way that permited an attacker to inject arbitrary SQL commands into the resulting SQL query. The PostgreSQL server has been modified to reject such invalidly encoded strings now, which completely fixes the problem for some 'safe' multibyte encodings like UTF-8. CVE-2006-2314: However, there are some less popular and client-only multibyte encodings (such as SJIS, BIG5, GBK, GB18030, and UHC) which contain valid multibyte characters that end with the byte 0x5c, which is the representation of the backslash character >>\<< in ASCII. Many client libraries and applications use the non-standard, but popular way of escaping the >>'<< character by replacing all occurrences of it with >>\'<<. If a client application uses one of the affected encodings and does not interpret multibyte characters, and a possible hacker supplies a specially crafted byte sequence as an input string parameter, this escaping method would then produce a validly-encoded character and an excess >>'<< character which would end the string. All subsequent characters would then be interpreted as SQL code, so the attacker could execute arbitrary SQL commands. To fix this vulnerability end-to-end, client-side applications must be fixed to properly interpret multibyte encodings and use >>''<< instead of >>\'<<. However, as a precautionary measure, the sequence >>\'<< is now regarded as invalid when one of the affected client encodings is in use. If you depend on the previous behavior, you can restore it by setting 'backslash_quote = on' in postgresql.conf. However, please be aware that this could render you vulnerable again. This issue does not affect you if you only use single-byte (like SQL_ASCII or the ISO-8859-X family) or unaffected multibyte (like UTF-8) encodings. Please see http://www.postgresql.org/docs/techdocs.50 for further details. Unfortunately we are not yet able to provide back ported patches for the PostgreSQL included in SUSE Linux Enterprise Server 8 at this time. We are working on a solution for this problem. Solution : http://www.suse.de/security/advisories/2006_30_postgresql.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

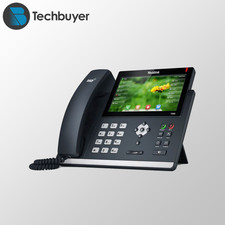
Yealink T48S VoIP/SIP Phone, 2 x Gigabit Ports PoE 7" Color SIP-T48S | TESTED
$34.95
Grandstream GXW4224 24-Line FXS Analog VoIP Gateway, Ethernet RJ-45 Black
$165.00
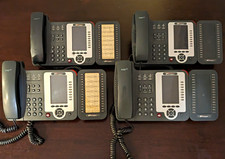
Lot of 4 USED IPitomy IP620-B with IPX-32 DSS Expansion Module VoIP Phone POE
$225.00
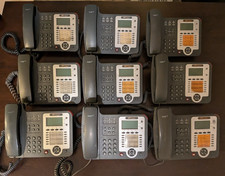
Lot of 9 Used IPitomy IP320-P HD POE Voice Speakerphone 12-Line VoIP Phone
$225.00
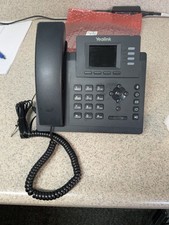
Yealink SIP-T33G IP Phone 4-LineSpeakerphone VoIP Desk Phone Black w/ Power Sply
$25.00
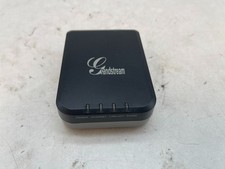
Grandstream HT701 1-Port FXS Analog Telephone Adapter ATA VoIP Gateway -Free S/H
$19.99
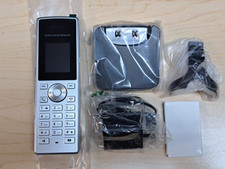
Grandstream WP810 Portable Cordless Wi-Fi IP Phone
$49.28

Cisco / Linksys SPA2102 VoIP 2FXS Phone Adapter with Router (unlocked)
$18.99
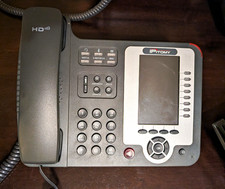
Set of 5 USED IPitomy IP620-B HD VoIP 6-Line IP Phone Speakerphone Ethernet POE
$149.00
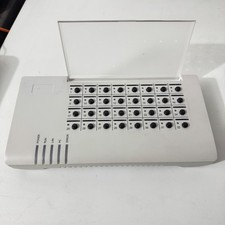
SIM Bank 32 SIM Card Slots Ethernet SIM Server for GoIP
$400.00
|
||
|
No Discussions have been posted on this vulnerability. |