|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SuSE Local Security Checks >> SUSE-SA:2006:006: kernel Vulnerability Assessment Details
|
SUSE-SA:2006:006: kernel |
||
|
Check for the version of the kernel package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory SUSE-SA:2006:006 (kernel). The Linux kernel on SUSE Linux 10.0 has been updated to fix following security problems: - CVE-2006-0454: An extra dst release when ip_options_echo failed was fixed. This problem could be triggered by remote attackers and can potentially crash the machine. This is possible even with SuSEfirewall2 enabled. This affects only SUSE Linux 10.0, all other SUSE distributions are not affected. - CVE-2005-3356: A double decrement in mq_open system call could lead to local users crashing the machine. - CVE-2005-3358: A 0 argument passed to the set_mempolicy() system call could lead to a local user crashing the machine. - CVE-2005-4605: Kernel memory could be leaked to user space through a problem with seek() in /proc files . - CVE-2005-3623: Remote users could set ACLs even on read-only exported NFS Filesystems and so circumvent access control. - CVE-2005-3808: A 32 bit integer overflow on 64bit mmap calls could be used by local users to hang the machine. - CVE-2005-4635: Add sanity checks for headers and payload of netlink messages, which could be used by local attackers to crash the machine. Also various non-security bugs were fixed: - Fix up patch for cpufreq drivers that do not initialize current freq. - Handle BIOS cpufreq changes gracefully. - Updates to inotify handling. - Various XEN Updates. - Catches processor declarations with same ACPI id (P4HT) - PowerPC: g5 thermal overtemp bug on fluid cooled systems. - Fixed buffered ACPI events on a lot ASUS and some other machines. - Fix fs/exec.c:788 (de_thread()) BUG_ON (OSDL 5170). Solution : http://www.suse.de/security/advisories/2006_06_kernel.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

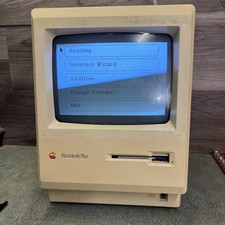
Apple Macintosh Plus 1MB M0001A Vintage Computer Boots Up / Floppy Disk Stuck
$99.99
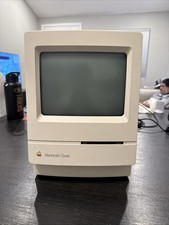
Apple Macintosh Classic M1420 Vintage Desktop Computer Model Macintosh Classic
$100.00
Vintage 1998 iMac G3 M4984 Mac OS + Keyboard Working but Needs Some Repair Read
$295.00
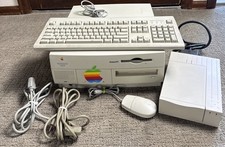
Apple Power Macintosh PowerPC 7300/200 VTG w Keyboard Mouse Storage Drive Read
$199.99
185--Sonnet Crescendo G3 PPCG3-375-5-K-06 G3 Add-On Card for Vintage Mac
$90.00
Vintage 1992 Mac System 7.1P1 Apple Software 3.5” Floppy Disks NOS
$35.00
READ - UNTESTED Apple Macintosh PowerBook 160 M4550 Vintage Laptop
$299.00
Macintosh MacTerminal M0521 Version 1.0. Vintage Apple software 1984 Sealed
$129.99
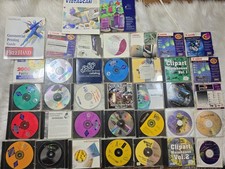
Mixed Lot Vintage Mac Windows media / Graphics / Sound Software - CDs 37 Pieces
$40.99
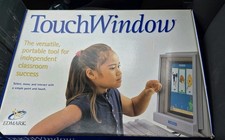
Vintage Edmark TouchWindow for Macintosh DeskTop Computer Touch Window Never Usd
$63.99
|
||
|
No Discussions have been posted on this vulnerability. |