|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SuSE Local Security Checks >> SUSE-SA:2005:068: kernel Vulnerability Assessment Details
|
SUSE-SA:2005:068: kernel |
||
|
Check for the version of the kernel package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory SUSE-SA:2005:068 (kernel). The Linux kernel was updated to fix several security problems and several bugs, listed below: Security fixes: - CVE-2005-3783: A check in ptrace(2) handling that finds out if a process is attaching to itself was incorrect and could be used by a local attacker to crash the machine. (All) - CVE-2005-3784: A check in reaping of terminating child processes did not consider ptrace(2) attached processes and would leave a ptrace reference dangling. This could lead to a local user being able to crash the machine. (Linux kernel 2.6 based products only) - CVE-2005-3806: A bug in IPv6 flow label handling code could be used by a local attacker to free non-allocated memory and in turn corrupt kernel memory and likely crash the machine. (All) - CVE-2005-3805: A locking problem in POSIX timer handling could be used by a local attacker on a SMP system to deadlock the machine. (SUSE Linux 9.3) - CVE-2005-3527: A race condition in do_coredump in signal.c permits local users to cause a denial of service (machine hang) by triggering a core dump in one thread while another thread has a pending SIGSTOP. (SUSE Linux 9.3) - CVE-2005-3807: A memory kernel leak in VFS lease handling can exhaust the machine memory and so cause a local denial of service. This is seen in regular Samba use and could also be triggered by local attackers. (SUSE Linux 9.3) - Others: see original advisory Solution : http://www.suse.de/security/advisories/2005_68_kernel.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

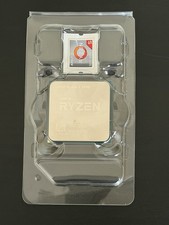
AMD Ryzen 5 5500 Processor ( read Description)
$59.00
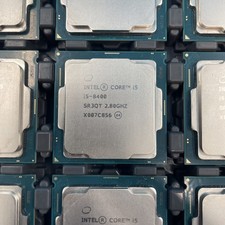
(LOT OF 20) Intel Core i5-8400 CPU 2.80GHz Desktop Processor (SR3QT)
$700.00
INTEL CORE I9-10940X X-SERIES PROCESSOR | 3.30GHZ | SRGSH
$179.99
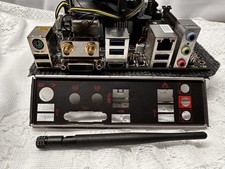
Compo MSI B150I GAMING PRO AC LGA1151 16 Gb DDR4 + Cpu I7 6700+I/O Shields.
$159.00
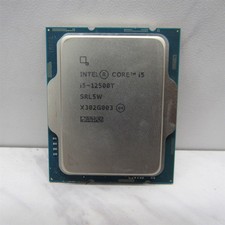
Intel Core i5-12500T SRL5W 2GHz 18MB 6 Core Socket LGA1700 Desktop CPU Processor
$114.99
Intel Core i7-9700 Octa-Core 3 GHz Desktop Processor LGA 1151
$79.99
Intel Core i7-3770K 3.5 GHz Processor
$39.00
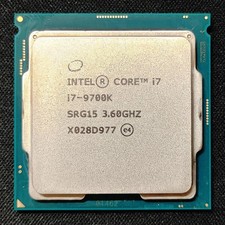
Intel Core i7-9700K Octa-Core 3.6 GHz Desktop CPU
$99.99
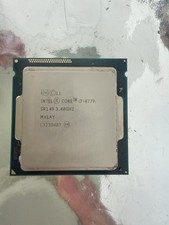
Intel Core i7-4770 3.40GHz Quad Core SR149 LGA 1150 CPU Processor tested
$35.00
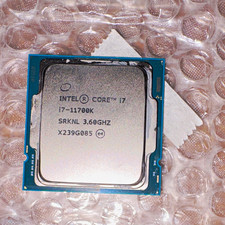
Intel Core i7-11700K 3.60GHz 11th Gen CPU Processor MPN SRKNL X239G085
$140.00
|
||
|
No Discussions have been posted on this vulnerability. |