|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SuSE Local Security Checks >> SUSE-SA:2005:045: mozilla,MozillaFirefox,epiphany,galeon Vulnerability Assessment Details
|
SUSE-SA:2005:045: mozilla,MozillaFirefox,epiphany,galeon |
||
|
Check for the version of the mozilla,MozillaFirefox,epiphany,galeon package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory SUSE-SA:2005:045 (mozilla,MozillaFirefox,epiphany,galeon). Various security vulnerabilities in the mozilla browser suite and the Mozilla Firefox browser have been reported and fixed upstream. The Mozilla suite browser has been updated to a security fix level of Mozilla 1.7.11, the Mozilla Firefox browser has been updated to a fix level of Firefox 1.0.6. Security relevant bugs that are fixed include (but are not limited to): MFSA 2005-56 Code execution through shared function objects MFSA 2005-55 XHTML node spoofing MFSA 2005-54 Javascript prompt origin spoofing MFSA 2005-52 Same origin violation: frame calling top.focus() MFSA 2005-51 The return of frame-injection spoofing MFSA 2005-50 Possibly exploitable crash in InstallVersion.compareTo() MFSA 2005-49 Stealing of sensitive information via _search and the Firefox sidebar MFSA 2005-48 Same-origin violation with InstallTrigger callback MFSA 2005-47 'Set as wallpaper' javascript: privilege escalation MFSA 2005-46 XBL scripts ran even when Javascript disabled MFSA 2005-45 Content-generated event vulnerabilities This update also upgrades the version of the Mozilla suite for the following products: * SUSE Linux Desktop 1.0: The original Mozilla 1.4 branch browser is upgraded to the Mozilla 1.7 branch version. We were not able to port the galeon web browser included in SUSE Linux Desktop 1.0 to support Mozilla 1.7 in time, so we no longer support it. The galeon package on SUSE Linux Desktop 1.0 is removed by this update. * SUSE Linux Enterprise Server 8: The original Mozilla 1.4 branch browser is upgraded to the Mozilla 1.7 branch version. * SUSE Linux Enterprise Server 9: The Mozilla version 1.6 shipped with GA of the SUSE Linux Enterprise Server 9 was replaced by the Mozilla 1.7 branch version in Service Pack 2. * SUSE Linux 8.2, 9.0, 9.1: The Mozilla version 1.4 and 1.6 contained in the SUSE Linux versions 8.2 up to 9.1 was replaced by the Mozilla 1.7 branch version. We were not able to port the galeon and the epiphany web browsers included in SUSE Linux 9.0 up to 9.1 to support Mozilla 1.7 in time, so we will no longer support it. The galeon and epiphany packages on SUSE Linux 9.0 and 9.1 are removed by this update. Solution : http://www.suse.de/security/advisories/2005_45_mozilla.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

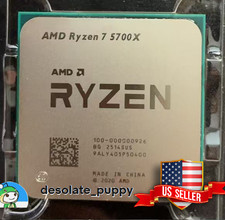
(New) AMD Ryzen 7 5700X 8 Core 16 Thread AM4 Unlocked 3.4 GHz CPU OEM Tray
$174.99
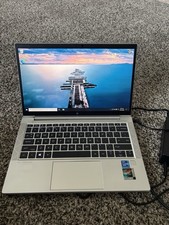
HP EliteBook 830 G8 Core I7-1185G7 3.00GHz Laptop 32GB RAM, 512GB SSD
$250.00
SGIN 17.3" Laptop Intel Quad-Core Up to 2.4 GHZ 8GB RAM 256GB SSD HD
$229.99
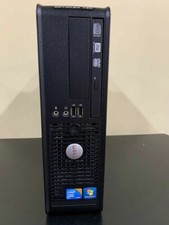
DELL Optiplex 780 SFF CORE2DUO 3.0GHz 8GB RAM 250GB HDDDVDRW NO OS
$99.99
AMD Ryzen 7 7800X3D 4.20GHz Quad Core 100-000000510 8 Thread AM4
$279.99
Intel Xeon E5 - 2667V2 / SR19W 3.30GHz 25MB 8-Core CPU Socket LGA2011
$30.00
Apple Macbook Pro 13" M1 8-Core 16GB 512GB - Good
$464.99
AMD Ryzen 7 9700X 8-Core 16-Thread 40MB Cache Socket AM5 9000 Series Processor
$245.99
Dell T7810 Workstation 8-Core 2.40GHz E5-2630 v3 No RAM GPU HDD OS
$259.98
Lenovo ThinkStation P520 Intel Xeon W-2245 8-Core 3.90GHz - NO RAM/ GPU/ HDD/ OS
$359.98
|
||
|
No Discussions have been posted on this vulnerability. |