|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SuSE Local Security Checks >> SUSE-SA:2005:044: kernel Vulnerability Assessment Details
|
SUSE-SA:2005:044: kernel |
||
|
Check for the version of the kernel package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory SUSE-SA:2005:044 (kernel). The Linux kernel is the core component of the Linux system. This update fixes various security as well as non-security problems discovered since the last round of kernel updates. Not all kernels are affected by all the problems, each of the problems has an affected note attached to it. The CAN-YYYY-NNNN IDs are Mitre CVE Candidate IDs, please see http://www.mitre.org for more information. The following security problems have been fixed: - local users could crash the system by causing stack fault exceptions (CVE-2005-1767) SUSE Linux 9.0 and SLES8 are affected. - local users could use ptrace to crash the kernel (CVE-2005-1761). SLES8 on the ia64 architecture is affected. - by causing an overflow in the 32bit execve function users could crash the kernel or even execute code (CVE-2005-1768). SLES 9 on the x86-64 and ia64 architectures and SUSE Linux 9.1 on the x86-64 architecture are affected. - an overflow when validating XDR data for the nfsacl protocol could crash the kernel. SUSE Linux 9.2 and 9.3 are affected. - local users could crash the kernel by reading from large offsets in sysfs files SUSE Linux 9.2 is affected. On SUSE Linux 9.1 this update contains the kernel used by the SUSE Linux Enterprise Server 9, Service Pack 2. This kernel adds among many bugfixes and driver updates support for non-executable pages (NX) on x86 CPUs and improves dual core CPU support. Solution : http://www.suse.de/security/advisories/2005_44_kernel.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

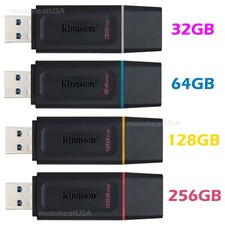
Kingston 32GB 64GB 128GB 256GB USB 3.0 Flash Drive Thumb Memory Stick Pen lot
$285.90
24x Micron MT40A512M16LY-062E IT:E 8Gb DDR4-3200 96-FBGA Memory IC
$349.99
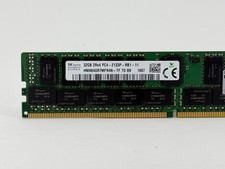
SK Hynix 32GB DDR4 2133MHz RDIMM Server Memory (HMA84GR7MFR4N-TF) - Preowned
$149.00
Microsoft Office 2021 Pro Plus USB for 1PC Windows 10 & 11
$62.55
USB 3.0 Flash Drive 32GB 64GB 128GB Memory Stick Thumb Stick Lot Pack
$826.09
USB 3.0 Micro SD SDHC TF Card Reader Memory Adapter for PC Laptop Camera lot
$3.75
3.5 lbs Lot of Assorted Ram Memory Sticks Mixed DDR Gold Recovery Scrap Untested
$165.00
Samsung 64GB PC4-2666V-R 2S2Rx4 DDR4 ECC REG RDIMM - M393A8K40B22-CWD6Y
$270.00
TF/SD Card Adapter Camera Reader Android Type-c For iPhone17 Pro Max Plusm lot
$573.98
1/ 10/ 100pcs USB 2.0 2GB, 4GB ,8GB ,16GB ,32GB ,64GB 128GB USB Flash Drives Lot
$202.50
|
||
|
No Discussions have been posted on this vulnerability. |