|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SuSE Local Security Checks >> SUSE-SA:2005:022: kdelibs3 Vulnerability Assessment Details
|
SUSE-SA:2005:022: kdelibs3 |
||
|
Check for the version of the kdelibs3 package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory SUSE-SA:2005:022 (kdelibs3). Several vulnerabilities have been identified and fixed in the KDE desktop environment. - A buffer overflow via specially crafted PCX pictures was fixed. This could lead to a remote attacker being able to execute code as the user opening or viewing a PCX images. This PCX image could have been embedded within a web page or Email. This affects SUSE Linux 9.1 up to 9.3, SUSE Linux Enterprise Server 9 and Novell Linux Desktop 9. - The IDN domain name cloaking problem was fixed. A remote website could disguise its name as another potentially trusted site by using a extension originally meant for non-ASCII domain names by using 'homographs' which look exactly like other letters. The fix used by KDE is only use homographs for trusted domains. It is disabled by default for the .net, .com and .org domains. This issue exists in SUSE Linux 9.1 and 9.2, SUSE Linux Enterprise Server 9 and Novell Linux Desktop 9. It has been assigned the Mitre CVE ID CVE-2005-0233. - A denial of service attack against the DCOP service was fixed. A local user could cause another users KDE session to visible hang by writing bad data to the world writable DCOP socket. The socket has been made writable only for the user itself. This was found by Sebastian Krahmer of SUSE Security. This affects all SUSE Linux versions, except SUSE Linux 9.3. Updates for SUSE Linux up to 9.0 and SUSE Linux Enterprise Server 8 are not included for this minor issue. They will be included should a later security update for different issues be necessary. This is tracked by the Mitre CVE ID CVE-2005-0396. Additionally following bug was fixed: - A possible race in the DNS resolver causing unresolved hosts in rare cases was fixed. This only affected SUSE Linux 9.3. Solution : http://www.suse.de/security/advisories/2005_22_kdelibs3.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

Apple Macintosh Plus 1MB M0001A Vintage Computer Boots Up / Floppy Disk Stuck
$99.99
Apple Macintosh Classic M1420 Vintage Desktop Computer Model Macintosh Classic
$100.00
Vintage 1998 iMac G3 M4984 Mac OS + Keyboard Working but Needs Some Repair Read
$295.00
Apple Power Macintosh PowerPC 7300/200 VTG w Keyboard Mouse Storage Drive Read
$199.99
Macintosh MacTerminal M0521 Version 1.0. Vintage Apple software 1984 Sealed
$129.99
Vintage 1992 Mac System 7.1P1 Apple Software 3.5” Floppy Disks NOS
$35.00
185--Sonnet Crescendo G3 PPCG3-375-5-K-06 G3 Add-On Card for Vintage Mac
$90.00
READ - UNTESTED Apple Macintosh PowerBook 160 M4550 Vintage Laptop
$299.00
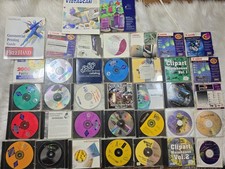
Mixed Lot Vintage Mac Windows media / Graphics / Sound Software - CDs 37 Pieces
$40.99
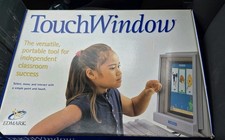
Vintage Edmark TouchWindow for Macintosh DeskTop Computer Touch Window Never Usd
$63.99
|
||
|
No Discussions have been posted on this vulnerability. |