|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SuSE Local Security Checks >> SUSE-SA:2005:019: mysql Vulnerability Assessment Details
|
SUSE-SA:2005:019: mysql |
||
|
Check for the version of the mysql package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory SUSE-SA:2005:019 (mysql). MySQL is an Open Source database server, commonly used together with web services provided by PHP scripts or similar. This security update fixes a broken mysqlhotcopy script as well as several security related bugs: - CVE-2005-0709: MySQL permited remote authenticated users with INSERT and DELETE rights to execute arbitrary code by using CREATE FUNCTION to access libc calls, as demonstrated by using strcat, on_exit, and exit. - CVE-2005-0710: MySQL permited remote authenticated users with INSERT and DELETE rights to bypass library path restrictions and execute arbitrary libraries by using INSERT INTO to modify the mysql.func table, which is processed by the udf_init function. - CVE-2005-0711: MySQL used predictable file names when creating temporary tables, which permits local users with CREATE TEMPORARY TABLE rights to overwrite arbitrary files via a symlink attack. The first two vulnerabilities can be exploited by a possible hacker using SQL inject attack vectors into a flawed PHP application for instance. Solution : http://www.suse.de/security/advisories/2005_19_mysql.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

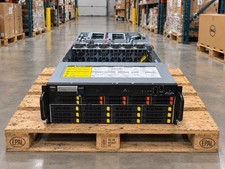
Gigabyte 4U AI Server 10x Nvidia GPU 2x Xeon Gold 6150 36 Core 2.7GHz DDR4 RAM
$1625.00

Dell EMC PowerEdge R440 Xeon silver 4215 2.5GHz 16 GB ram 2x 550W PSU No HDD
$275.00
867959-B21 HPE ProLiant DL360 G10 CTO Server W/ 2x 865414-B21 1x 840140-001
$245.00

Dell PowerEdge R240 Intel Xeon E-2224 3.50GHz 8GB DDR4 ECC NO HDD 250W
$285.97
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2680 v3 | 32gb Ram | 2x 1600W
$409.99

Dell PowerEdge R730XD 28 Core Server 2X Xeon E5-2680 V4 H730 32GB RAM No HDD
$378.93
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2690 v3 | 64gb Ram | 2x 1600W
$524.99
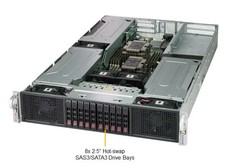
Supermicro 2U GPU Server SYS-2029GP-TR 2x Xeon 6130 32C 6x PCIe 3.0 x16 Slots
$745.00

Dell PowerEdge R530 2x E5-2630v4 H330 iDRAC8 Port Card Riser No PSU/RAM/HDD
$99.99

Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00
|
||
|
No Discussions have been posted on this vulnerability. |