|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SuSE Local Security Checks >> SUSE-SA:2005:003: kernel Vulnerability Assessment Details
|
SUSE-SA:2005:003: kernel |
||
|
Check for the version of the kernel package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory SUSE-SA:2005:003 (kernel). Several exploitable security problems were identified and fixed in the Linux kernel, the core of every SUSE Linux product. - Due to missing locking in the sys_uselib system call a local attacker can gain root access. This was found by Paul Starzetz and is tracked by the Mitre CVE ID CVE-2004-1235. - Paul Starzetz also found a race condition in SMP page table handling which could lead to a local attacker gaining root access on SMP machines. This is tracked by the Mitre CVE ID CVE-2005-0001. - A local denial of service was found in the auditing subsystem which have lead a local attacker crashing the machine. This was reported and fixed by Redhat. - The sendmsg / cmsg fix from the previous kernel update was faulty on 64bit systems with 32bit compatibility layer and could lead to 32bit applications not working correctly on those 64bit systems. - The smbfs security fixes from a before-previous kernel update were faulty for some file write cases. - A local denial of service with Direct I/O access to NFS file systems could lead a local attacker to crash a machine with NFS mounts. - grsecurity reported a signed integer problem in the SCSI ioctl handling which had a missing boundary check. Due to C language specifics, this evaluation was not correct and there actually is no problem in this code. The signed / unsigned mismatch was fixed nevertheless. - Several more small non security problems were fixed. NOTE: Two days ago we released the Service Pack 1 for the SUSE Linux Enterprise Server 9. This kernel update contains fixes for the SUSE Linux Enterprise Server 9 GA version kernel line. A fix for the Service Pack 1 version line will be available shortly. Solution : http://www.suse.de/security/advisories/2005_03_kernel.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

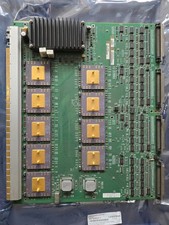
Vintage DEC E2052-AA AlphaServer I/O Board 9 Gold Ceramic ICs 4.3 LB Gold Scrap
$729.99
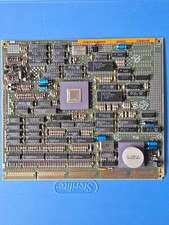
Vintage DEC Digital T1043 DWMBB/B VAXBI XMI Adapter 5018232-01 C1 VAX Board
$109.99
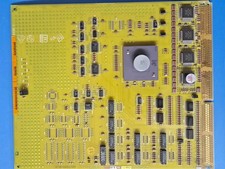
Vintage DEC Digital XMI-A1 5017293-01A1 LWPR BE3-0 VAX Circuit Board T2012
$74.99
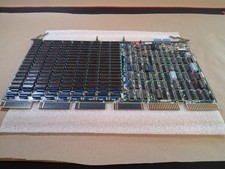
Vintage DEC/Mostek memory systems MK 8015 AA-00 6805-08015 1100 REV C(B7)
$279.99
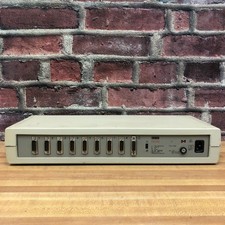
Vintage DEC Digital Equipment DELNI 8-Port Ethernet Local Network Hub VAXstation
$79.95
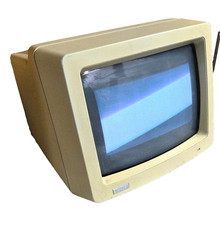
Vintage Digital VR241-A color CRT monitor, powers on, DEC Rainbow or terminal
$150.00
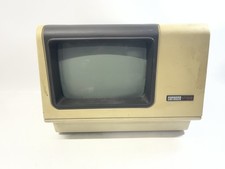
Vintage DEC VT100 Series Terminal (Powers On)
$499.99
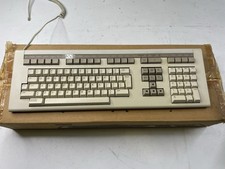
Vintage DEC LK201 Digital Equipment Corporation (DEC) LK201-AA Computer Keyboard
$149.99
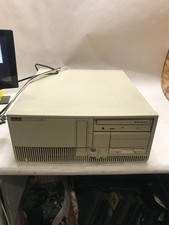
Vintage DEC Digital Starion 200 Desktop PC Powers On Boots To BIOS NO HDD - DW
$269.99
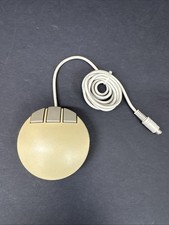
Vintage DEC Digital VSXXX-AA.B03 Hawley 3-Button Mouse 1986 Tested Working
$111.00
|
||
|
No Discussions have been posted on this vulnerability. |