|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SuSE Local Security Checks >> SUSE-SA:2004:020: kernel Vulnerability Assessment Details
|
SUSE-SA:2004:020: kernel |
||
|
Check for the version of the kernel package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory SUSE-SA:2004:020 (kernel). Multiple security vulnerabilities are being addressed with this security update of the Linux kernel. Kernel memory access vulnerabilities are fixed in the e1000, decnet, acpi_asus, alsa, airo/WLAN, pss and mpu401 drivers. These vulnerabilities can lead to kernel memory read access, write access and local denial of service conditions, resulting in access to the root account for a possible hacker with a local account on the affected system. Missing Discretionary Access Control (DAC) checks in the chown(2) system call permit a possible hacker with a local account to change the group ownership of arbitrary files, which leads to root rights on affected systems. It is specific to kernel version 2.6 based systems such as the SUSE Linux 9.1 product, that only local shell access is needed to exploit this vulnerability. An interesting variant of the missing checks is that the ownership of files in the /proc filesystem can be altered, while the changed ownership still does not permit the files to be accessed as a non-root user for to be able to exploit the vulnerability. Systems that are based on a version 2.4 kernel are not vulnerable to the /proc weakness, and exploitation of the weakness requires the use of the kernel NFS server (knfsd). If the knfsd NFS server is not activated (it is off by default), the vulnerability is not exposed. These issues related to the chown(2) system call have been discovered by Michael Schroeder and Ruediger Oertel, both SUSE LINUX. The only network-related vulnerability fixed with the kernel updates that are subject to this announcement affect the SUSE Linux 9.1 distribution only, as it is based on a 2.6 kernel. Found and reported to bugtraq by Adam Osuchowski and Tomasz Dubinski, the vulnerability permits a remote attacker to send a specially crafted TCP packet to a vulnerable system, causing that system to stall if it makes use of TCP option matching netfilter rules. In some rare configurations of the SUSE Linux 9.1 distribution, some users have experienced stalling systems during system startup. These problems are fixed with this kernel update. Solution : http://www.suse.de/security/2004_20_kernel.html Network Security Threat Level: High Networks Security ID: 10352, 10566, 10779 Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

AMD Ryzen 5 5500 Processor ( read Description)
$59.00
(LOT OF 20) Intel Core i5-8400 CPU 2.80GHz Desktop Processor (SR3QT)
$700.00
INTEL CORE I9-10940X X-SERIES PROCESSOR | 3.30GHZ | SRGSH
$179.99
Compo MSI B150I GAMING PRO AC LGA1151 16 Gb DDR4 + Cpu I7 6700+I/O Shields.
$159.00
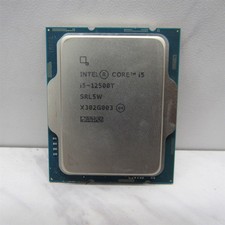
Intel Core i5-12500T SRL5W 2GHz 18MB 6 Core Socket LGA1700 Desktop CPU Processor
$114.99
Intel Core i7-9700 Octa-Core 3 GHz Desktop Processor LGA 1151
$79.99
Intel Core i7-3770K 3.5 GHz Processor
$39.00
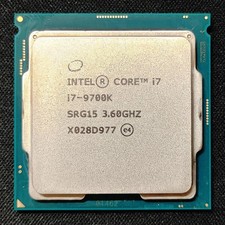
Intel Core i7-9700K Octa-Core 3.6 GHz Desktop CPU
$99.99
Intel Core i7-4770 3.40GHz Quad Core SR149 LGA 1150 CPU Processor tested
$35.00
INTEL CORE I9-10980XE PROCESSOR | 3.00GHZ | SRGSG
$299.99
|
||
|
No Discussions have been posted on this vulnerability. |