|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SuSE Local Security Checks >> SUSE-SA:2003:043: openssl Vulnerability Assessment Details
|
SUSE-SA:2003:043: openssl |
||
|
Check for the version of the openssl package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory SUSE-SA:2003:043 (openssl). OpenSSL is an implementation of the Secure Socket Layer (SSL v2/3) and Transport Layer Security (TLS v1) protocol. While checking the openssl implementation with a tool-kit from NISCC several errors were revealed most are ASN.1 encoding issues that causes a remote denial-of-service attack on the server side and possibly lead to remote command execution. There are two problems with ASN.1 encoding that can be triggered either by special ASN.1 encodings or by special ASN.1 tags. In debugging mode public key decoding errors can be ignored but also lead to a crash of the verify code if an invalid public key was received from the client. A mistake in the SSL/TLS protocol handling will make the server accept client certificates even if they are not requested. This bug makes it possible to exploit the bugs mentioned above even if client authentication is disabled. There is not other solution known to this problem then updating to the current version from our FTP servers. To make this update effective, restart all servers using openssl please. Please download the update package for your distribution and verify its integrity by the methods listed in section 3) of this announcement. Then, install the package using the command 'rpm -Fhv file.rpm' to apply the update. Solution : http://www.suse.de/security/2003_043_openssl.html Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

GIGABYTE A520M DS3H AC AMD AM4 Motherboard mATX
$59.99
GIGABYTE Z790 AORUS ELITE AX LGA 1700 Intel Z790 ATX Motherboard with DDR5
$189.99
Intel H310 LGA1151 8-9th Gen DDR4 M.2 NVMe mATX Motherboard IO Shield Battery
$54.99
ASUS PRIME Z490-V Motherboard Intel Z490 10th gen DDR4 LGA 1200 ATX w/ IO Shield
$84.99
GIGABYTE B365 HD3 LGA1151 Intel 9th Gen motherboard
$59.99
Intel H81 Motherboard M.2 NVMe LGA 1150 mATX w/ IO Shield (Random Slot Color)
$29.90
ASUS PRIME B360M-C MicroATX Intel LGA1151 DDR4 HDMI VGA USB RJ-45 Audio
$34.99
ASUS TUF GAMING B550-PLUS WIFI II AM4 AMD B550 ATX AMD Motherboard
$95.99
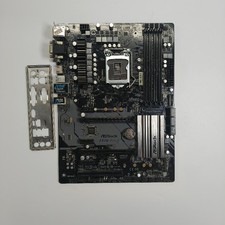
ASRock Z370 Pro4 LGA 1151 Z370 HDMI USB 3.1 2 Ultra M.2 DDR4 ATX Motherboard
$75.00
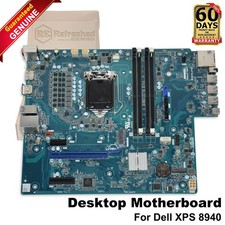
Dell XPS 8940 Desktop Motherboard Intel H470 LGA1200 DDR4 K3CM7 KV3RP 427JK
$154.99
|
||
|
No Discussions have been posted on this vulnerability. |