|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SuSE Local Security Checks >> SUSE-SA:2003:013: sendmail, sendmail-tls Vulnerability Assessment Details
|
SUSE-SA:2003:013: sendmail, sendmail-tls |
||
|
Check for the version of the sendmail, sendmail-tls package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory SUSE-SA:2003:013 (sendmail, sendmail-tls). sendmail is the most widely used mail transport agent (MTA) in the internet. A remotely exploitable buffer overflow has been found in all versions of sendmail that come with SUSE products. These versions include sendmail-8.11 and sendmail-8.12 releases. sendmail is the MTA subsystem that is installed by default on all SUSE products up to and including SUSE LINUX 8.0 and the SUSE LINUX Enterprise Server 7. The vulnerability is triggered by an email message sent through the sendmail MTA subsystem. In that respect, it is different from commonly known bugs that occur in the context of an open TCP connection. By consequence, the vulnerability also exists if email messages get forwarded over a relay that itself does not run a vulnerable MTA. This specific detail and the wide distribution of sendmail in the internet causes this vulnerability to be considered an error of major severity. The buffer overflow happens on the heap and is known to be exploitable. As of the writing of this announcement, there is no exploit known to exist in the public. Since there is no known workaround for this vulnerability other than using a different MTA, it is strongly recommended to install the update packages as offered at the locations as listed below. We would like to express our gratitude to Eric Allman for notifying SUSE Security of the problem. The vulnerability was discovered by ISS Internet Security Systems, inc. Please download the update package for your distribution and verify its integrity by the methods listed in section 3) of this announcement. Then, install the package using the command 'rpm -Fhv file.rpm' to apply the update. Solution : http://www.suse.de/security/2003_13_sendmail.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

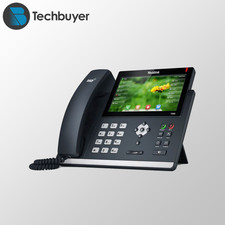
Yealink T48S VoIP/SIP Phone, 2 x Gigabit Ports PoE 7" Color SIP-T48S | TESTED
$34.95
Grandstream GXW4224 24-Line FXS Analog VoIP Gateway, Ethernet RJ-45 Black
$165.00
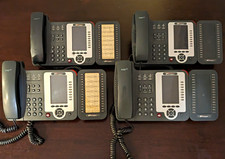
Lot of 4 USED IPitomy IP620-B with IPX-32 DSS Expansion Module VoIP Phone POE
$225.00
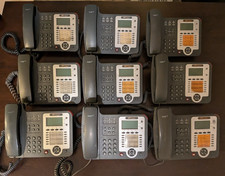
Lot of 9 Used IPitomy IP320-P HD POE Voice Speakerphone 12-Line VoIP Phone
$225.00
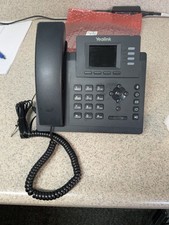
Yealink SIP-T33G IP Phone 4-LineSpeakerphone VoIP Desk Phone Black w/ Power Sply
$25.00
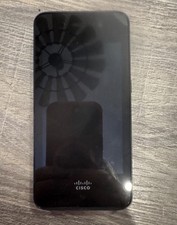
NEW Cisco CP-840 Wireless WiFi IP VoIP Phone 840 w Battery Charger Cable
$800.00
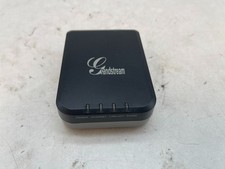
Grandstream HT701 1-Port FXS Analog Telephone Adapter ATA VoIP Gateway -Free S/H
$19.99
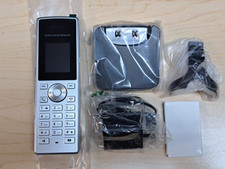
Grandstream WP810 Portable Cordless Wi-Fi IP Phone
$49.28
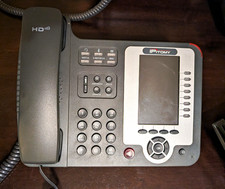
Set of 5 USED IPitomy IP620-B HD VoIP 6-Line IP Phone Speakerphone Ethernet POE
$149.00
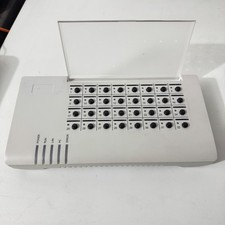
SIM Bank 32 SIM Card Slots Ethernet SIM Server for GoIP
$400.00
|
||
|
No Discussions have been posted on this vulnerability. |