|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SuSE Local Security Checks >> SUSE-SA:2003:0010: libmcrypt Vulnerability Assessment Details
|
SUSE-SA:2003:0010: libmcrypt |
||
|
Check for the version of the libmcrypt package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory SUSE-SA:2003:0010 (libmcrypt). Libmcrypt is a data encryption library that is able to load crypto- modules at run-time by using libltdl. Versions of libmcrypt prior to 2.5.5 include several buffer overflows that can be triggered by passing very long input to the mcrypt_* functions. The way libmcrypt handles dynamic crypto-modules via libltdl leads to memory-leaks that can cause a Denial-of-Service condition. This Problem can just be solved by linking modules static. This security update does not solve the memory-leak problem to avoid compatibility problems. Future releases of libmcrypt will be linked statically. To add the new library to the shared library cache you have to run ldconfig(8) as root. Additionally every program that is linked with libmcrypt needs to be restarted. ldd(1) can be used to find out which libraries are used by a program. Another way to acertain which process uses a shared library that had been deleted is: lsof -n 2>/dev/null | grep RPMDELETE | cut -d ' ' -f 1 | sort | uniq There is no temporary fix known. Please install the new packages from our FTP servers. Please download the update package for your distribution and verify its integrity by the methods listed in section 3) of this announcement. Then, install the package using the command 'rpm -Fhv file.rpm' to apply the update. Solution : http://www.suse.de/security/2003_010_libmcrypt.html Network Security Threat Level: Medium Networks Security ID: 6510, 6512 Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

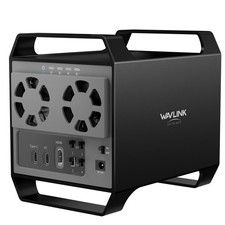
2-Bay/4-Bay Hard Drive Enclosure for 3.5"/2.5'' SATA HDD/SSD 10Gbps USB-C 3.2
$75.99

OWC Mercury Elite Pro 2 Bay RAID Enclosure with USB 3.2 for Dual 3.5 inch HDDs
$87.99
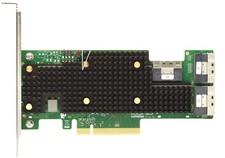
Broadcom 9600-24i RAID Controller PCIe Gen 4.1 Tri-Mode NEW 05-50111-01004
$649.99
Intel VROC Premium RAID Controller Card PCIe Add-On Module VROCPREMMOD
$265.00
Acasis USB 3.2 2 Bay HDD RAID Enclosure for 2.5/3.5" SATA Drives External Array
$55.00
MegaRAID 9580-8i8e 16-port 12G SAS/SATA/NVMe 8GB PCIe RAID - 05-50076-00
$1619.19
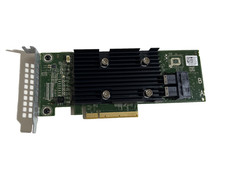
Dell PowerEdge HBA330 LP PCI-E 12GBs RAID SAS Controller Adapter J7TNV
$18.95
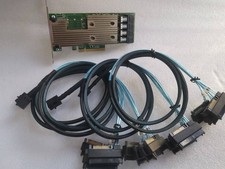
LSI 9305-16i SATA SAS 12Gbs Controller card PCIe 3.0 IT-Mode w/SAS SATA cable US
$125.98
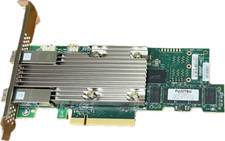
Broadcom MegaRAID 9480-8e Fujitsu PRAID EP540e SAS RAID Card (Replac 9380-8e) 8i
$228.00
Intel® Integrated RAID Mezzanine Module RMS3HC080 SAS/SATA H24093-204
$24.97
|
||
|
No Discussions have been posted on this vulnerability. |