|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SuSE Local Security Checks >> SUSE-SA:2002:040: lprng, html2ps Vulnerability Assessment Details
|
SUSE-SA:2002:040: lprng, html2ps |
||
|
Check for the version of the lprng, html2ps package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory SUSE-SA:2002:040 (lprng, html2ps). The lprng package contains the 'runlpr' program which permits the lp user to execute the lpr program as root. Local attackers can pass certain commandline arguments to lpr running as root, fooling it to execute arbitrary commands as root. This has been fixed. Note that this vulnerability can only be exploited if the attacker has previously gained access to the lp account. Additionally, the html2ps printfilter, which is installed as part of the LPRng print system, permited remote attackers to execute arbitrary commands in the context of the lp user. These two issues combined permit attackers to mount a remote root attack. As a workaround, we recommend to uninstall the html2ps package, and restrict access to your print services to authorized hosts only. Access control to lpd is implemented by adding appropriate entries to the /etc/lpd.perms file. Please consult the lpd.perms(5) manpage, or add the single line DEFAULT REJECT to your /etc/lpd.perms file to deny access to everyone from the outside. Please download the update package for your distribution and verify its integrity by the methods listed in section 3) of this announcement. Then, install the package using the command 'rpm -Fhv file.rpm' to apply the update. Solution : http://www.suse.de/security/2002_040_lprng_html2ps.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

Kingston 32GB 64GB 128GB 256GB USB 3.0 Flash Drive Thumb Memory Stick Pen lot
$285.90
Lot of 4 8GB DDR4 PC4-2400T ECC Registered Server RAM 32GB 1Rx8 RDIMM MICRON
$149.99
1/ 10/ 100pcs USB 2.0 2GB, 4GB ,8GB ,16GB ,32GB ,64GB 128GB USB Flash Drives Lot
$202.50
Microsoft Office 2021 Pro Plus USB for 1PC Windows 10 & 11
$62.55
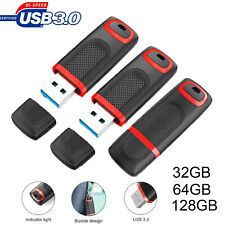
USB 3.0 Flash Drive 32GB 64GB 128GB Memory Stick Thumb Stick Lot Pack
$826.09
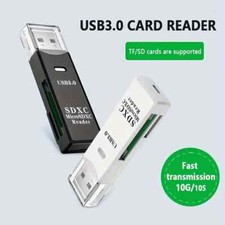
USB 3.0 Micro SD SDHC TF Card Reader Memory Adapter for PC Laptop Camera lot
$3.75
Samsung M391A1K43BB2-CTDQ 4 x 8GB 1Rx8 PC4-2666V DDR4 UDIMM RAM Memory
$140.00
Server Memory: Samsung 32GB 4DRx4 PC4-2133P ECC LRDIMM DDR4 M386A4G40DM0-CPB
$124.95
4x8GB Samsung DDR4 2133MHz PC4-2133P 1Rx4 ECC Registered Server RAM 32GB Sansumg
$149.99
TF/SD Card Adapter Camera Reader Android Type-c For iPhone17 Pro Max Plusm lot
$573.98
|
||
|
No Discussions have been posted on this vulnerability. |