|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Slackware Local Security Checks >> SSA-2006-155-01 mysql Vulnerability Assessment Details
|
SSA-2006-155-01 mysql |
||
|
SSA-2006-155-01 mysql Detailed Explanation for this Vulnerability Assessment New mysql packages are available for Slackware 9.1, 10.0, 10.1, 10.2 and -current to fix security issues. The MySQL packages shipped with Slackware 9.1, 10.0, and 10.1 may possibly leak sensitive information found in uninitialized memory to authenticated users. This is fixed in the new packages, and was already patched in Slackware 10.2 and -current. Since the vulnerabilities require a valid login and/or access to the database server, the risk is moderate. Slackware does not provide network access to a MySQL database by default. More details about the issues may be found in the Common Vulnerabilities and Exposures (CVE) database. Fixes that affect Slackware 9.1, 10.0, and 10.1: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-1516 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-1517 The MySQL packages in Slackware 10.2 and -current have been upgraded to MySQL 4.1.20 (Slackware 10.2) and MySQL 5.0.22 (Slackware -current) to fix an SQL injection vulnerability. For more details, see the MySQL 4.1.20 release announcement here: http://lists.mysql.com/announce/364 And the MySQL 5.0.22 release announcement here: http://lists.mysql.com/announce/365 The CVE entry for this issue can be found here: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-2753 Here are the details from the Slackware 10.1 ChangeLog: +--------------------------+ patches/packages/mysql-4.0.27-i486-1_slack10.1.tgz: Upgraded to mysql-4.0.27. This fixes some minor security issues with possible information leakage. Note that the information leakage bugs require that the attacker have access to an account on the database. Also note that by default, Slackware's rc.mysqld script does *not* permit access to the database through the outside network (it uses the --skip-networking option). If you've enabled network access to MySQL, it is a good idea to filter the port (3306) to prevent access from unauthorized machines. For more details, see the MySQL 4.0.27 release announcement here: http://lists.mysql.com/announce/359 For more information, see: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-1516 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-1517 (* Security fix *) +--------------------------+ Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Michel Arboi |
||
|
Cables, Connectors |

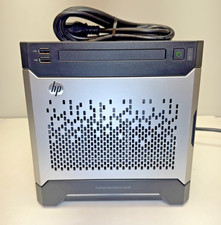
HP ProLiant MicroServer Gen8 G1610T @2.3 GHz, 16GB, 712317-001 NO HDD/OS
$199.00
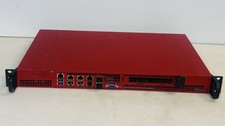
Supermicro 1U Network Server Appliance 16GB RAM 800GB SSD 6 LAN Ports Powers On
$450.00
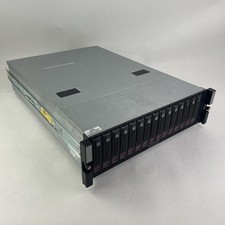
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
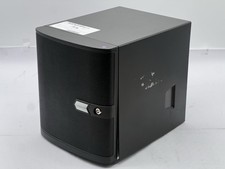
Nasuni NF-50 Supermicro Server, Atom CPU C2558, @ 2.40GHz, 8GB RAM-No HDD/OS/AC
$250.00
New Barebones Supermicro 5019D Server, 4C/8T Xeon D-2123T, 1U Rackmountable, 10G
$449.99
Supermicro 2U X10DRU-i 2x E5-2680 v3 2.5ghz 32gb Ram 240gb SSD 2x GPU *READ*
$369.99
Supermicro 5019D-4C-FN8TP Xeon D-2123IT (4C/8T) 64GB DDR4 10GbE 480GB 1U Server
$689.00
Supermicro 1027GR-TSF 1U Rackmount Server 2x Xeon 2.3GHz 128GB DDR3
$219.99
$280.00
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
|
||
|
No Discussions have been posted on this vulnerability. |