|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Service detection >> SOAP Server Detection Vulnerability Assessment Details
|
SOAP Server Detection |
||
|
Detects a SOAP Server Detailed Explanation for this Vulnerability Assessment Summary : There is a SOAP server listening on the remote host. Description : The remote host is running a SOAP server. SOAP, originally an acronym for 'Simple Object Access Protocol', is an XML-based distributed messaging protocol typically implemented over HTTP. See also : http://en.wikipedia.org/wiki/SOAP http://www.w3.org/TR/soap12-part0/ Solution : Limit incoming traffic to this port if desired. Network Security Threat Level: None Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |
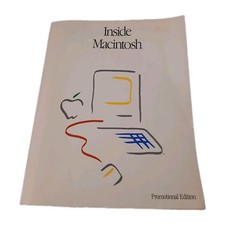
Inside Macintosh Promotional Edition Vintage Apple Developer Book 1985
$32.00
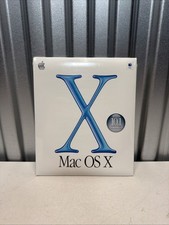
NEW Vintage Apple Mac OS X Version 10.1 Upgrade CD 2001 Factory Sealed Package
$29.95
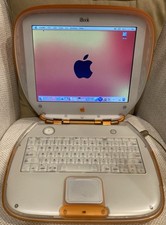
Vintage Apple iBook Clamshell Tangerine OS 9 & 10
$500.00
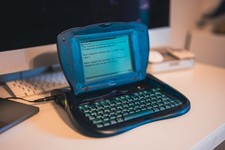
Apple eMate 300 H0208 Newton Laptop 1997 Tested Working w/ Stylus Vintage
$159.99
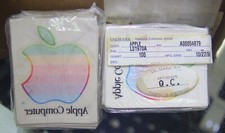
One (1) VINTAGE APPLE STATIC "NO GLUE" RAINBOW STICKER NEW
$4.99
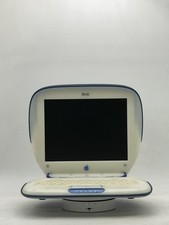
Apple iBook M6411 G3 Clamshell Laptop Vintage Untested AS-IS
$149.99
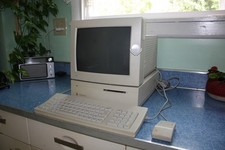
Vintage Apple Macintosh IIsi Computer, Monitor, Keyboard & Mouse Complete Setup
$199.99
Vintage Apple Extended Keyboard II M3501 Mechanical ADB - Tested & Working
$54.99
Vintage Apple Macintosh Power PC 7200 / 120 Power PC Tested Works Read Desc
$159.95
Apple cloth fabric banner iBook tangerine orange New Old Stock Vintage
$99.00
|
||
|
No Discussions have been posted on this vulnerability. |