|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2007-0013: kernel Vulnerability Assessment Details
|
RHSA-2007-0013: kernel |
||
|
Check for the version of the kernel packages Detailed Explanation for this Vulnerability Assessment Updated kernel packages that fix a number of security issues as well as other bugs are now available for Red Hat Enterprise Linux 2.1 (32 bit architectures) This security advisory has been rated as having moderate security impact by the Red Hat Security Response Team. The Linux kernel handles the basic functions of the operating system. These new kernel packages contain fixes for the security issues described below: * a flaw in the ATM subsystem affecting systems with installed ATM hardware and configured ATM support that permited a remote user to cause a denial of service (panic) by accessing socket buffer memory after it has been freed (CVE-2006-4997, Moderate) * a flaw in the DVD handling of the CDROM driver that could be used together with a custom built USB device to gain root rights (CVE-2006-2935, Moderate) In addition to the security issues described above, the following bugs are also addressed: * a potential overflow condition when reading /proc/devices * uninitialized memory in cdrom_init() that can lead to a crash at install time * a potential page corruption bug in /proc/kcore * a race condition when reading vmalloc()ed regions via /proc/kcore All Red Hat Enterprise Linux 2.1 users are advised to upgrade their kernels to these updated packages, which contain backported fixes to correct these issues. Solution : http://rhn.redhat.com/errata/RHSA-2007-0013.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2007 Tenable Network Security |
||
|
Cables, Connectors |

Lenovo ThinkPad E14 Gen 2 Laptop 14” HD Ryzen 5 16GB RAM 512GB SSD Win 11 Pro
$334.99
Lenovo ThinkPad L15 Gen 3 15.6" 16GB, Thunder Black
$241.50
Lenovo ThinkPad E14 Gen 3 Laptop 14” FHD AMD Ryzen 5 16GB RAM 512GB SSD Win 11
$374.99
Lenovo Thinkbook 14s Yoga ITL 14” Core i7-1165G7, 16GB RAM, 512GB SSD Touch
$379.00
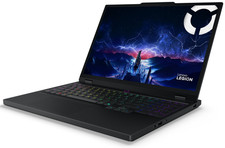
Lenovo Legion 5 Gaming 15.1" WQXGA OLED 165Hz Core i9-14900HX 16GB 1TB RTX 5070
$1469.00
Lenovo ThinkPad T14 Gen 1 14" AMD Ryzen 5 16GB 256GB SSD
$219.99
Lenovo ThinkPad X13 Gen 1 i5-10310U 16GB 512GB SSD Touch Win 11 Pro Good
$222.99
Lenovo - IdeaPad Slim 3i 15.3" 2K Touchscreen Laptop - Intel Core 7 350 2026 ...
$679.99
Lenovo ThinkPad L15 Gen 3 15.6" 16GB, Thunder Black
$241.50
Lenovo ThinkPad T495 14” Laptop AMD Ryzen 5 PRO 16GB RAM 256GB SSD Windows 11
$229.99
|
||
|
No Discussions have been posted on this vulnerability. |