|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0760: thunderbird Vulnerability Assessment Details
|
RHSA-2006-0760: thunderbird |
||
|
Check for the version of the thunderbird packages Detailed Explanation for this Vulnerability Assessment Updated thunderbird packages that fix several security bugs are now available for Red Hat Enterprise Linux 4. This update has been rated as having critical security impact by the Red Hat Security Response Team. Mozilla Thunderbird is a standalone mail and newsgroup client. Several flaws were found in the way Thunderbird processes certain malformed Javascript code. A malicious web page could cause the execution of Javascript code in such a way that could cause Thunderbird to crash or execute arbitrary code as the user running Thunderbird. JavaScript support is disabled by default in Thunderbird this issue is not exploitable without enabling JavaScript. (CVE-2006-6498, CVE-2006-6501, CVE-2006-6502, CVE-2006-6503, CVE-2006-6504) Several flaws were found in the way Thunderbird renders web pages. A malicious web page could cause the browser to crash or possibly execute arbitrary code as the user running Thunderbird. (CVE-2006-6497) A heap based buffer overflow flaw was found in the way Thunderbird parses the Content-Type mail header. A malicious mail message could cause the Thunderbird client to crash or possibly execute arbitrary code as the user running Thunderbird. (CVE-2006-6505) Users of Thunderbird are advised to apply this update, which contains Thunderbird version 1.5.0.9 that corrects these issues. Solution : http://rhn.redhat.com/errata/RHSA-2006-0760.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |


Crucial MX500 1TB 2.5" SATA III Internal SSD CT1000MX500SSD1
$99.99

Samsung 2.5" 870 EVO SSD SATA III 250GB 500GB 1TB Internet Solid State Drive Lot
$90.00
Samsung New SSD 970 EVO Plus 2TB 1TB 500GB 250GB NVMe M2 Internal Hard Drive Lot
$79.99
Netac 120GB 256GB 1TB 2TB Internal SSD 2.5'' SATAIII 6Gb/s Solid State Drive lot
$119.99

Netac 2TB 1TB 512GB 256GB Internal SSD 2.5inch SATAIII Solid State Drive lot
$549.00
Crucial MX500 250GB 2.5" SATA III SSD - Preowned
$29.00
Samsung 256 GB Internal SATA SSD Fully Tested 50%-79% Health
$24.00
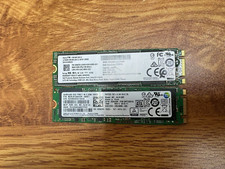
2 PACK 128 GB SSD M.2 2280 SATA Solid State Drive Major Brands, Samsung, LiteON
$28.00
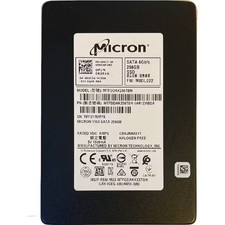
Micron MTFDDAK256TBN 256 GB, Internal ,2.5" SSD
$23.00
EDILOCA EN880E 1TB M.2 NVMe PCIe Gen4 Internal SSD for Laptop/PC
$115.00
|
||
|
No Discussions have been posted on this vulnerability. |