|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0759: seamonkey Vulnerability Assessment Details
|
RHSA-2006-0759: seamonkey |
||
|
Check for the version of the seamonkey packages Detailed Explanation for this Vulnerability Assessment Updated seamonkey packages that fix several security bugs are now available for Red Hat Enterprise Linux 2.1, 3, and 4. This update has been rated as having critical security impact by the Red Hat Security Response Team. SeaMonkey is an open source Web browser, advanced email and newsgroup client, IRC chat client, and HTML editor. Several flaws were found in the way SeaMonkey processes certain malformed Javascript code. A malicious web page could cause the execution of Javascript code in such a way that could cause SeaMonkey to crash or execute arbitrary code as the user running SeaMonkey. (CVE-2006-6498, CVE-2006-6501, CVE-2006-6502, CVE-2006-6503, CVE-2006-6504) Several flaws were found in the way SeaMonkey renders web pages. A malicious web page could cause the browser to crash or possibly execute arbitrary code as the user running SeaMonkey. (CVE-2006-6497) A heap based buffer overflow flaw was found in the way SeaMonkey Mail parses the Content-Type mail header. A malicious mail message could cause the SeaMonkey Mail client to crash or possibly execute arbitrary code as the user running SeaMonkey Mail. (CVE-2006-6505) Users of SeaMonkey are advised to upgrade to these erratum packages, which contain SeaMonkey version 1.0.7 that corrects these issues. Solution : http://rhn.redhat.com/errata/RHSA-2006-0759.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

Commodore 128 C128 Computer FOR PARTS / REPAIR Untested Missing Key No Cords
$149.99
TeensyROM+ TR+ v0.4 Cartridge for C64/128 - w/ Case & 32GB SD Preloaded
$89.50
Commodore VIC-20 Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
RARE Commodore MPS801 Printer - 1st printer for the 64 - powers on
$70.00
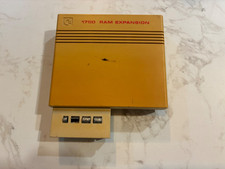
Commodore 1750 512K RAM Expansion REU for C128 / C64 – Tested & Working
$110.00
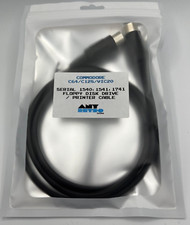
Commodore 64 Serial Cable 6PIN DIN 1541 1571 C64 128 C128 Disk Drive Printer USA
$10.49
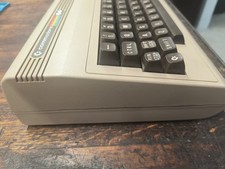
Commodore 64 C64 Breadbin Computer System TESTED READ
$159.00
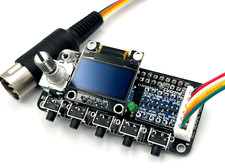
Commodore 1541 Emulator PI1541 HAT with ROTARY, OLED screen, USA Seller
$29.99
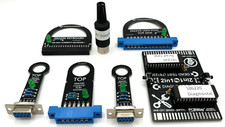
Commodore 64 Dead Test & Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
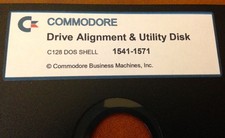
Commodore 64 Drive Alignment & Utility Diskette
$9.99
|
||
|
No Discussions have been posted on this vulnerability. |