|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0734: seamonkey Vulnerability Assessment Details
|
RHSA-2006-0734: seamonkey |
||
|
Check for the version of the seamonkey packages Detailed Explanation for this Vulnerability Assessment Updated seamonkey packages that fix several security bugs are now available for Red Hat Enterprise Linux 2.1, 3, and 4. This update has been rated as having critical security impact by the Red Hat Security Response Team. SeaMonkey is an open source Web browser, advanced email and newsgroup client, IRC chat client, and HTML editor. Several flaws were found in the way SeaMonkey processes certain malformed Javascript code. A malicious web page could cause the execution of Javascript code in such a way that could cause SeaMonkey to crash or execute arbitrary code as the user running SeaMonkey. (CVE-2006-5463, CVE-2006-5747, CVE-2006-5748) Several flaws were found in the way SeaMonkey renders web pages. A malicious web page could cause the browser to crash or possibly execute arbitrary code as the user running SeaMonkey. (CVE-2006-5464) A flaw was found in the way SeaMonkey verifies RSA signatures. For RSA keys with exponent 3 it is possible for a possible hacker to forge a signature that would be incorrectly verified by the NSS library. SeaMonkey as shipped trusts several root Certificate Authorities that use exponent 3. An attacker could have created a carefully crafted SSL certificate which be incorrectly trusted when their site was visited by a victim. This flaw was previously thought to be fixed in SeaMonkey 1.0.5, however Ulrich Kuehn discovered the fix was incomplete (CVE-2006-5462) Users of SeaMonkey are advised to upgrade to these erratum packages, which contains SeaMonkey version 1.0.6 that corrects these issues. Solution : http://rhn.redhat.com/errata/RHSA-2006-0734.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

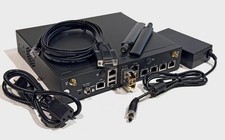
OPNsense pfSense 8-Core Atom C3758 2.2GHz 8GB DDR4 64GB SSD 8x NIC QAT AES VPN
$155.00
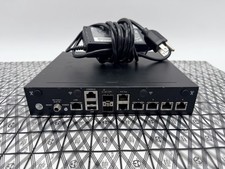
pfSense Firewall 16-Core Atom C3958 8GB DDR4 RAM 64GB SSD 8x 1Gbe QAT AES-NI VPN
$184.99
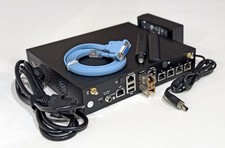
OPNsense pfSense 16-Core Atom C3958 16GB ECC RAM 512GB SSD 8-Port QAT AES-NI VPN
$248.00
SonicWall TZ280 Firewall 03-SSC-6933 Advanced Edition 3YR NEW SEALED
$999.99
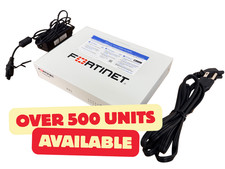
Fortinet FortiGate 60F FG-60F P24286-03-13 Network Firewall Security Appliance
$155.75
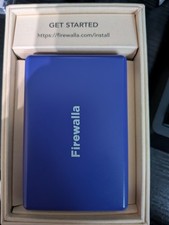
Firewalla Purple SE Cyber Security Firewall Home Business VPN…
$215.00
FortiGate-60F Network Security Firewall Fortinet - Used
$95.00
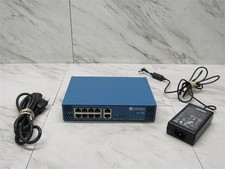
Palo Alto PA-220 Next-Gen Firewall 520-000309-00J
$40.00
NETGEAR ProSafe 8-Port Gigabit VPN Firewall FVS318G NEW IN BOX
$69.99
Cisco Meraki MX67-HW Security Appliance Firewall NEW Unused Unclaimed
$202.50
|
||
|
No Discussions have been posted on this vulnerability. |