|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0733: firefox Vulnerability Assessment Details
|
RHSA-2006-0733: firefox |
||
|
Check for the version of the firefox packages Detailed Explanation for this Vulnerability Assessment Updated firefox packages that fix several security bugs are now available for Red Hat Enterprise Linux 4. This update has been rated as having critical security impact by the Red Hat Security Response Team. Mozilla Firefox is an open source Web browser. Several flaws were found in the way Firefox processes certain malformed Javascript code. A malicious web page could cause the execution of Javascript code in such a way that could cause Firefox to crash or execute arbitrary code as the user running Firefox. (CVE-2006-5463, CVE-2006-5747, CVE-2006-5748) Several flaws were found in the way Firefox renders web pages. A malicious web page could cause the browser to crash or possibly execute arbitrary code as the user running Firefox. (CVE-2006-5464) A flaw was found in the way Firefox verifies RSA signatures. For RSA keys with exponent 3 it is possible for a possible hacker to forge a signature that would be incorrectly verified by the NSS library. Firefox as shipped trusts several root Certificate Authorities that use exponent 3. A possible hacker could have created a carefully crafted SSL certificate which be incorrectly trusted when their site was visited by a victim. This flaw was previously thought to be fixed in Firefox 1.5.0.7, however Ulrich Kuehn discovered the fix was incomplete (CVE-2006-5462) Users of Firefox are advised to upgrade to these erratum packages, which contain Firefox version 1.5.0.8 that corrects these issues. Solution : http://rhn.redhat.com/errata/RHSA-2006-0733.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

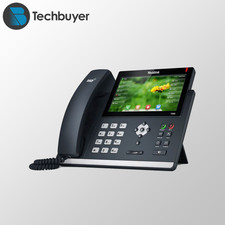
Yealink T48S VoIP/SIP Phone, 2 x Gigabit Ports PoE 7" Color SIP-T48S | TESTED
$34.95
Grandstream GXW4224 24-Line FXS Analog VoIP Gateway, Ethernet RJ-45 Black
$165.00
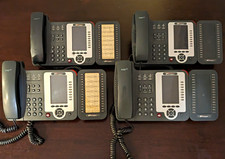
Lot of 4 USED IPitomy IP620-B with IPX-32 DSS Expansion Module VoIP Phone POE
$225.00
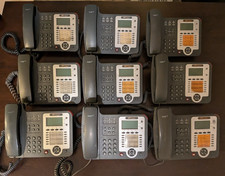
Lot of 9 Used IPitomy IP320-P HD POE Voice Speakerphone 12-Line VoIP Phone
$225.00
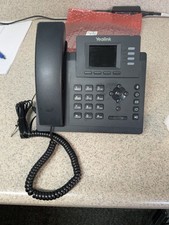
Yealink SIP-T33G IP Phone 4-LineSpeakerphone VoIP Desk Phone Black w/ Power Sply
$25.00
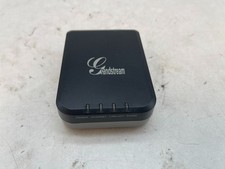
Grandstream HT701 1-Port FXS Analog Telephone Adapter ATA VoIP Gateway -Free S/H
$19.99
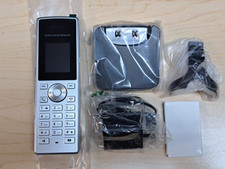
Grandstream WP810 Portable Cordless Wi-Fi IP Phone
$49.28

Cisco / Linksys SPA2102 VoIP 2FXS Phone Adapter with Router (unlocked)
$18.99
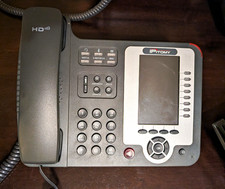
Set of 5 USED IPitomy IP620-B HD VoIP 6-Line IP Phone Speakerphone Ethernet POE
$149.00
SIM Bank 32 SIM Card Slots Ethernet SIM Server for GoIP
$400.00
|
||
|
No Discussions have been posted on this vulnerability. |