|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0719: nss_ldap Vulnerability Assessment Details
|
RHSA-2006-0719: nss_ldap |
||
|
Check for the version of the nss_ldap packages Detailed Explanation for this Vulnerability Assessment Updated nss_ldap packages that fix a security flaw are now available for Red Hat Enterprise Linux 4. This update has been rated as having moderate security impact by the Red Hat Security Response Team. nss_ldap is a set of C library extensions that permit X.500 and LDAP directory servers to be used as primary sources for aliases, ethers, groups, hosts, networks, protocols, users, RPCs, services, and shadow passwords. A flaw was found in the way nss_ldap handled a PasswordPolicyResponse control sent by an LDAP server. If an LDAP server responded to an authentication request with a PasswordPolicyResponse control, it was possible for an application using nss_ldap to improperly authenticate certain users. (CVE-2006-5170) This flaw was only exploitable within applications which did not properly process nss_ldap error messages. Only xscreensaver is currently known to exhibit this behavior. All users of nss_ldap should upgrade to these updated packages, which contain a backported patch that resolves this issue. Solution : http://rhn.redhat.com/errata/RHSA-2006-0719.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

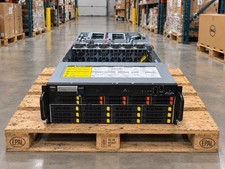
Gigabyte 4U AI Server 10x Nvidia GPU 2x Xeon Gold 6150 36 Core 2.7GHz DDR4 RAM
$1625.00

Dell EMC PowerEdge R440 Xeon silver 4215 2.5GHz 16 GB ram 2x 550W PSU No HDD
$275.00
867959-B21 HPE ProLiant DL360 G10 CTO Server W/ 2x 865414-B21 1x 840140-001
$245.00

Dell PowerEdge R240 Intel Xeon E-2224 3.50GHz 8GB DDR4 ECC NO HDD 250W
$285.97

Dell PowerEdge R730XD 28 Core Server 2X Xeon E5-2680 V4 H730 32GB RAM No HDD
$378.93
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2690 v3 | 64gb Ram | 2x 1600W
$524.99
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2680 v3 | 32gb Ram | 2x 1600W
$409.99
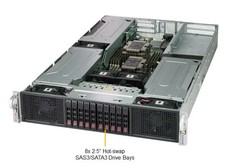
Supermicro 2U GPU Server SYS-2029GP-TR 2x Xeon 6130 32C 6x PCIe 3.0 x16 Slots
$745.00

Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00

Dell PowerEdge R530 2x E5-2630v4 H330 iDRAC8 Port Card Riser No PSU/RAM/HDD
$99.99
|
||
|
No Discussions have been posted on this vulnerability. |